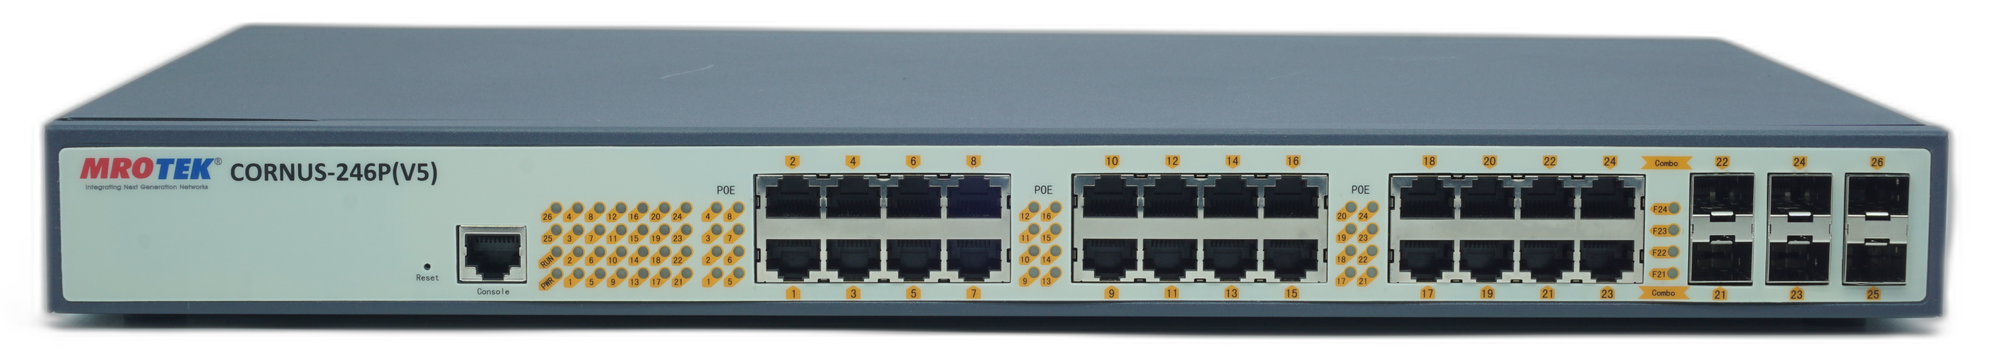
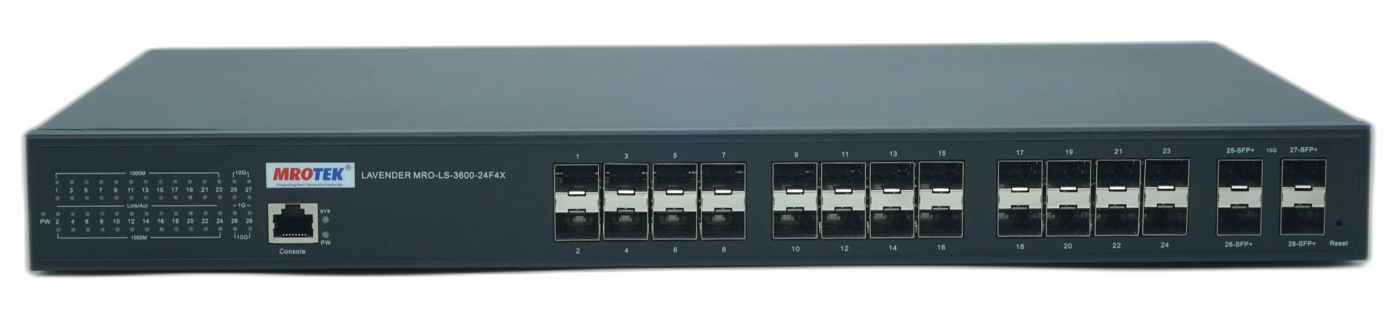
LAVENDER Layer 3 Switches
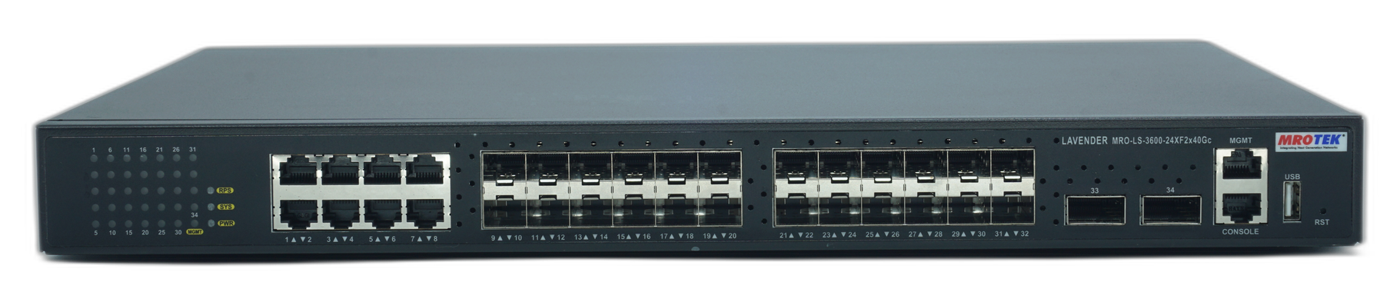
LAVENDER Layer 3 series — Layer 3 managed, static routing, RIP, OSPF, up to 40GE uplinks.
LAVENDER Layer 2 Switches
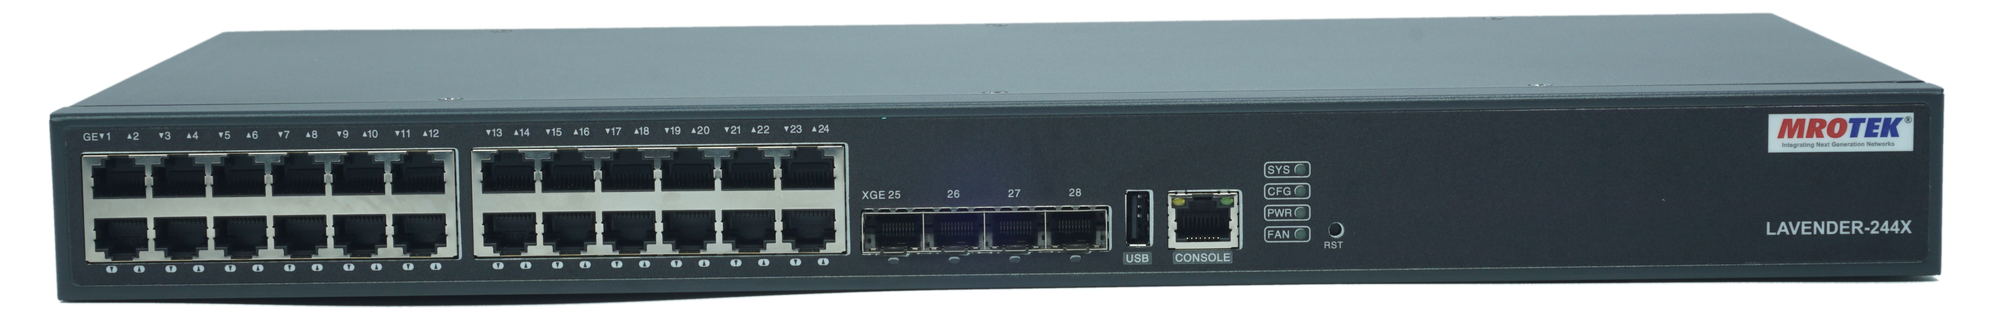
LAVENDER series — Layer 2 managed, 128 Gbps non-blocking, 16K MAC, 10G Ether-ring.
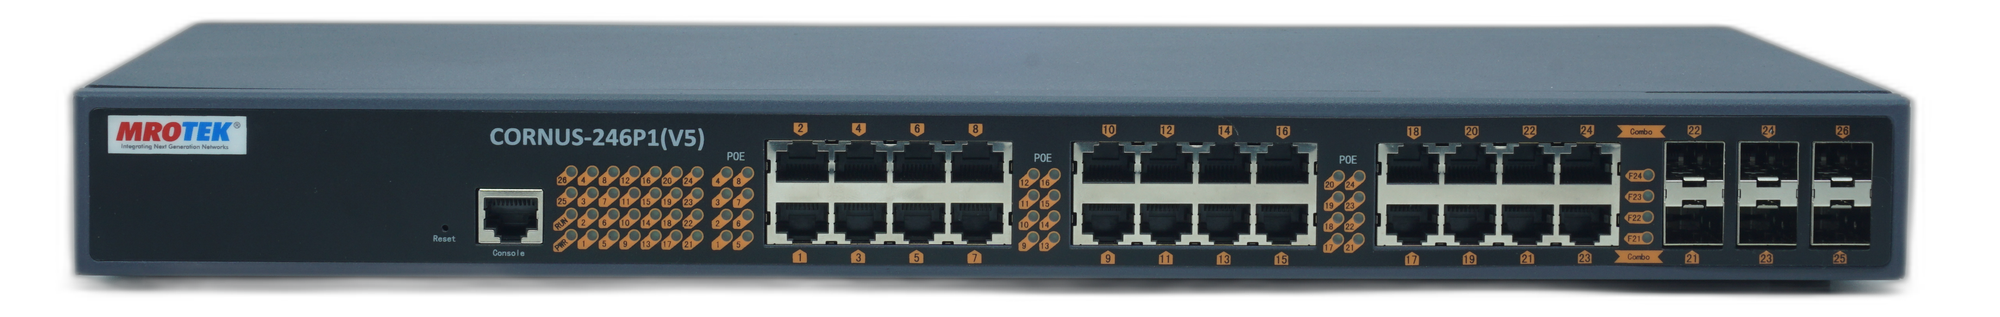
CORNUS LAYER 2 SWITCHES
CORNUS series — full Layer 2 managed, GbE access with SFP uplinks, PoE up to 450W.
L3 Routing
Static routing, RIP v2, and OSPF v2 for inter-VLAN routing and campus core/aggregation without a separate router.
Ether-ring Protection
10G Ether-ring backbone protection for fast ring redundancy at the aggregation/core layer.
Layer 2 Protocols
802.1D (STP), 802.1W (RSTP), and 802.1S (MSTP) spanning tree with root/BPDU guard, LLDP/LLDP-MED and UDLD for topology discovery, plus IEEE 802.3ad LACP link aggregation.
Management & Monitoring
CLI, Telnet, SSH v1/v2, and Web GUI management with SNMP v1/v2c/v3 — RADIUS/TACACS+ AAA and ACL policy control included.
Layer 2 Protocols
802.1D/W/S spanning tree (STP/RSTP/MSTP) with root/BPDU guard, 802.1Q VLAN with QinQ, LACP link aggregation, and 10G Ether-ring (ERPS) backbone ring protection.
Management & Monitoring
CLI, Telnet, SSH v2, and Web GUI management with SNMP v1/v2c/v3 and RMON — centrally managed via OmniEye NMS/EMS.
PoE+
IEEE 802.3af/at PoE+ on PoE-capable models — up to 24 ports, 370W total budget — power IP phones, cameras, and APs directly.
Port Security
IEEE 802.1x port and MAC-based authentication with RADIUS/TACACS+, ACL policy control, port isolation/security, and IP Source Guard with IP-MAC port binding.
Management & Monitoring
Console, Telnet, SSH v2, and Web GUI management with SNMP v1/v2c/v3 and RMON — optionally managed via OmniEye NMS/EMS.
Layer 2 Protocols
IEEE 802.1Q VLAN, QinQ, and private VLAN; LACP link aggregation with port mirroring; STP/RSTP/MSTP with BPDU and root guard; IGMP snooping v1/v2/v3; policy-based ACL by VLAN, MAC, IP, or port.
PoE
IEEE 802.3af/at PoE+ on CORNUS-82P/162P/246P models — up to 450W total PoE budget to power APs, cameras, and IP phones directly.
Port Security
Storm control for broadcast, multicast, and unicast traffic, with port security, MAC address binding, IP-MAC port binding, and 802.1x/RADIUS/TACACS+ authentication.
Models
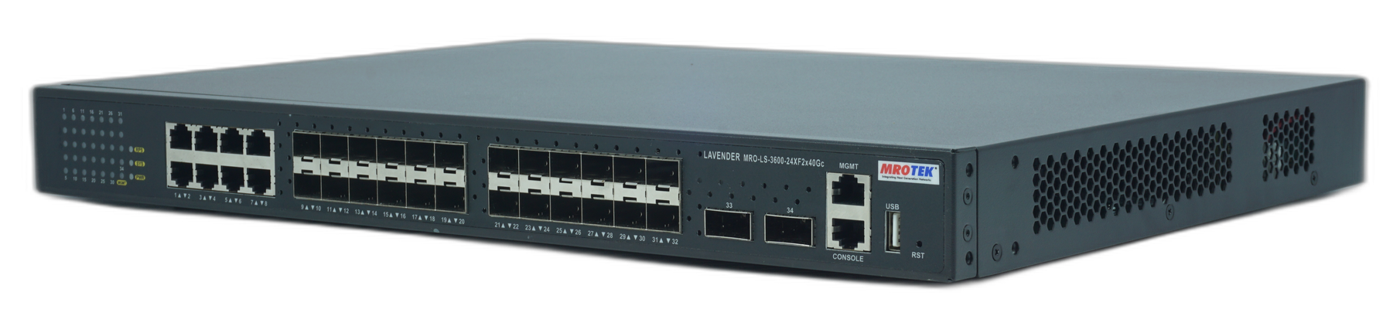
- 8× 10/100/1000BaseT copper ports
- 24× 10GE fiber ports
- 2× 40GE uplink ports
- 1× RJ-45 console port
- 1U rack-mountable form factor
- DVMRP, PIM-DM, PIM-SM, PIM-SSM, Anycast RP, MSDP
- Static multicast route, multicast receive control
- Illegal multicast source detection
- ARP Guard, local ARP proxy, proxy ARP, ARP binding
- Gratuitous ARP, ARP limit
- Anti ARP/NDP cheat, anti ARP/NDP scan
- DNS client, DNS relay
- ICMPv6, ND, DNSv6, VRRPv3, URPF, RA
- MLD snooping, multicast VLAN
- MLD v1/v2, PIM-SM/DM, Anycast RP, ACL, QoS
- DHCP server/client for IPv4/IPv6
- DHCP relay/option 82, DHCP snooping
- Port loopback detection, LLDP and LLDP-MED, UDLD
- IEEE 802.3ad LACP — up to 128 trunk groups, max 8 ports per trunk, LACP load balancing
- N:1 port mirroring, RSPAN
- 802.1D (STP), 802.1W (RSTP), 802.1S (MSTP), root guard, BPDU guard
- 802.1Q — 4K VLAN
- MAC VLAN, voice VLAN, PVLAN, protocol VLAN, multicast VLAN
- QinQ, selective QinQ, flexible QinQ
- GVRP, broadcast/multicast/unicast storm control
- Humidity: 5%–90% non-condensing
- Operating temperature: 0°C to 50°C
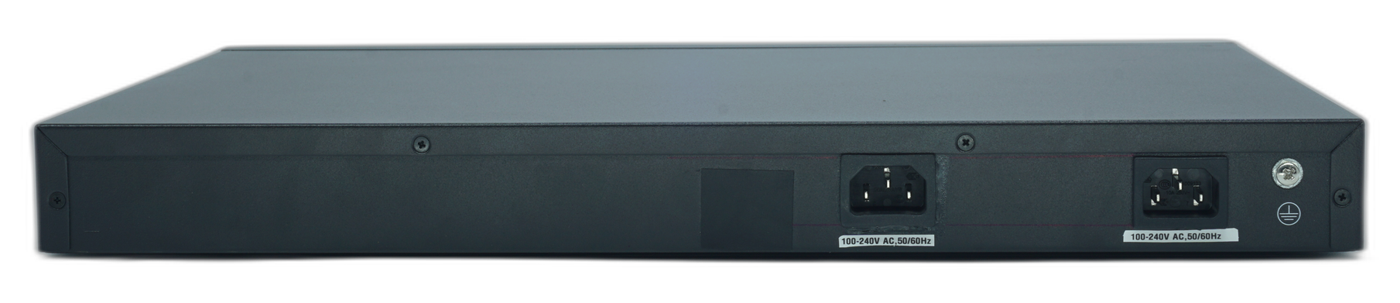
- Power supply — dual AC+DC or dual AC+AC configurations
- Power consumption: <85W
- Storm control — broadcast/multicast/unicast
- Port isolation, port security
- IP Source Guard and IP MAC port binding
- Authentication — IEEE 802.1x, RADIUS and TACACS+
- CLI, Web, Telnet, HTTPS/SSL, SSH v1/v2
- SNMP v1/v2c/v3, SNMP MIB, SNMP trap
- RMON groups 1, 2, 3, and 9, syslog and external syslog server
- FTP/TFTP, SNTP/NTP, RADIUS/TACACS
- Dual firmware images/configuration files
- 802.3ah OAM, 802.1ag OAM, sFlow
- 8 queues — SWRR, SP, WRR, WDRR, SWDRR scheduling
- Traffic classification based on 802.1p CoS, ToS, DiffServ, DSCP, ACL, port number
- Traffic policing, priority mark/remark
- MRO-LS-3600-24XF2x-40Gc — Managed L3 40G uplink Switch, 8× 10/100/1000Base-T (RJ45) + 24× 10GE + 2× 40GbE, dual AC+DC or dual AC+AC power supply configurations
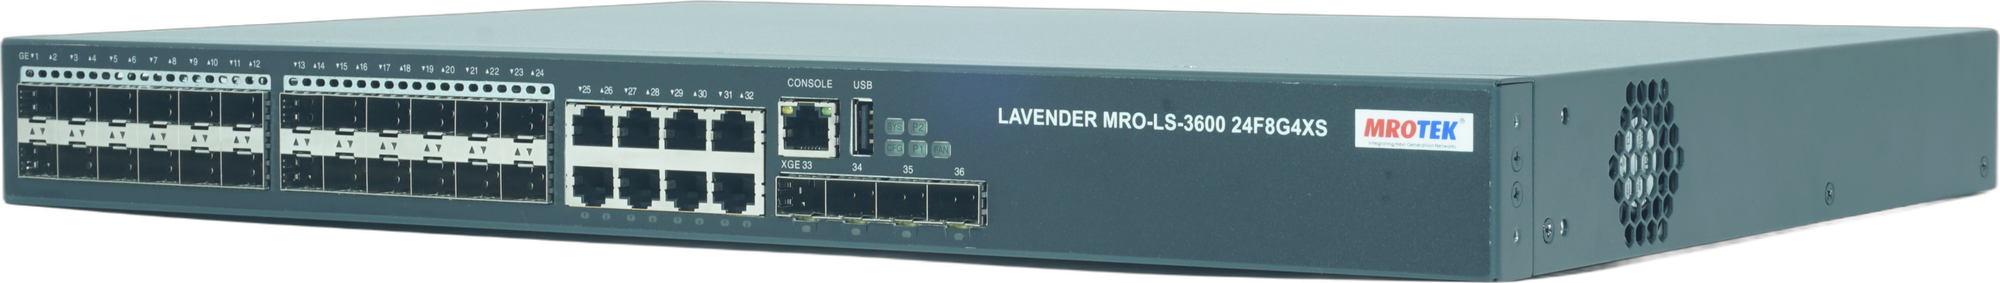
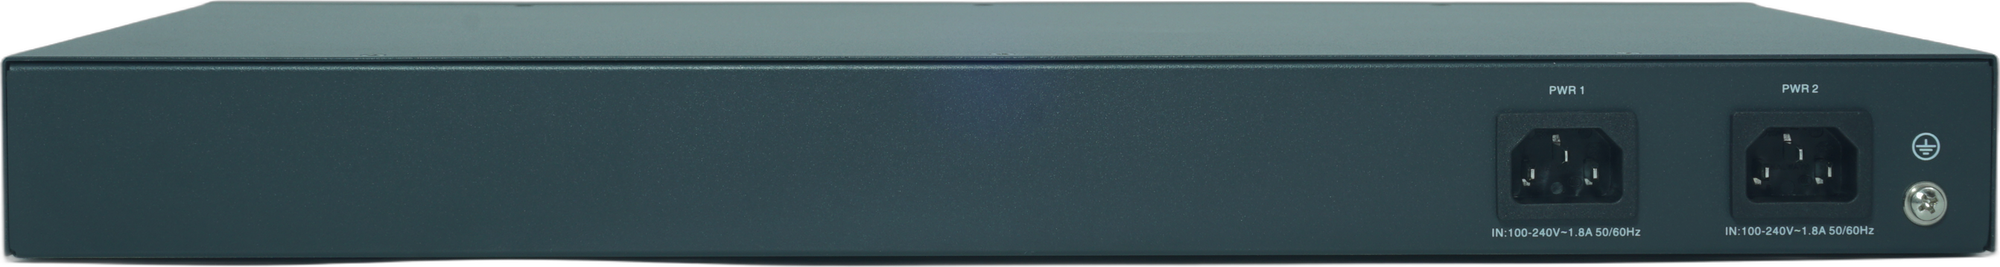
- 24/48× GE + 4× 1G/10G uplink slots
- Power options: AC, DC, PoE
- Port ingress/egress rate limiting
- Port speed: auto-negotiate, full-10000/2500/1000/100, half-100, full-10/half-10
- 1× RJ-45 console port
- 1U rack-mountable, stacking-capable via uplink slots
- Port loop detection, EAPS (RFC 3619)
- ERPS (G.8032/Y.1344), LLDP-MED, UDLD
- VLLP (VRRP Layer-2 loop protection)
- Static multicast MAC address
- IGMP snooping v1/v2/v3
- IGMP querier, IGMP snooping filter, MVR, GMRP, IGMP, PIM-SM
- 802.1Q-based VLAN, MAC-based VLAN, IP-based VLAN, protocol-based VLAN, PVLAN, voice VLAN
- VLAN mapping, QinQ, GVRP
- MAC table capacity and management, IVL forwarding mode
- Static MAC address, MAC address binding
- MAC address filtering, MAC learning control
- Management access security — Telnet, SSH, HTTP, HTTPS, SNMP bound to standard IP ACLs
- IP-MAC binding — static configuration of IP, MAC, and port binding
- AAA — RADIUS, TACACS+, 802.1x, portal
- CPU protection against large data-stream attacks
- Standard and extended IP-based ACL
- MAC IP-based ACL, MAC ARP-based ACL
- ACL port filtering, time-based ACL
- DHCP client, DHCP snooping
- DHCP relay, DHCP server, DHCP option 82
- CLI, Web, SNMP management, user management
- TACACS+, password encryption (PAP/CHAP), syslog logging
- RMON groups 1, 2, 3, and 9
- Cluster management
- Configuration file and software upgrade via TFTP
- Clock management via SNTP
- 8 port queues — WRR, WFQ, SP scheduling
- Port-based, 802.1p-based, DSCP-based, and ACL-based classification
- QoS policy support
- LAVENDER MRO-LS-3600-244XS — Managed L3 Switch, 24× GE + 4× 1G/10G uplink slots, Power AC, PoE (option)
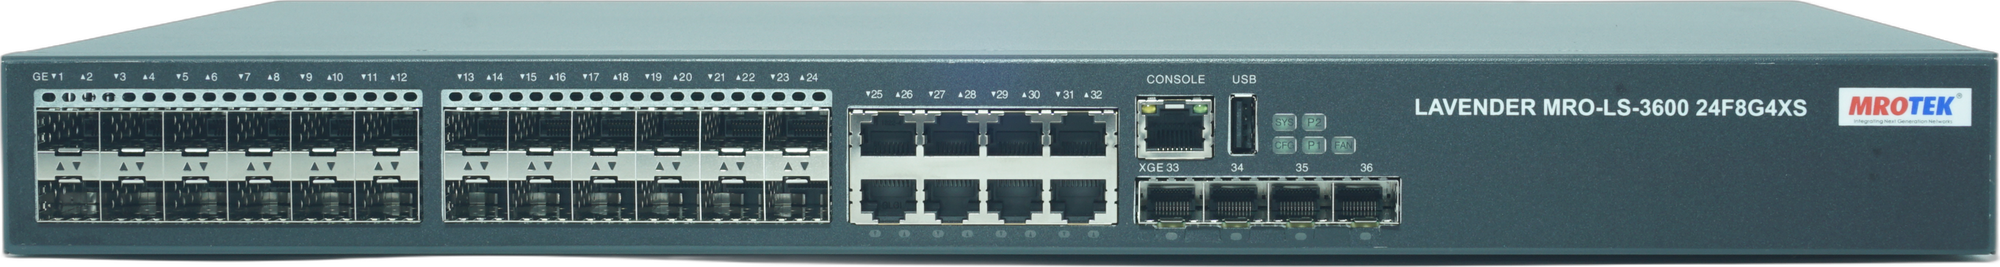
- LAVENDER MRO-LS-3600-24F8G4XS — Managed L3 Switch, 24× 1G Fiber + 8× GE + 4× 1G/10G uplink slots, Power AC
- LAVENDER MRO-LS-3600-486X — Managed L3 Switch, 48× GE + 6× 1G/10G uplink slots, PoE (option), AC Power
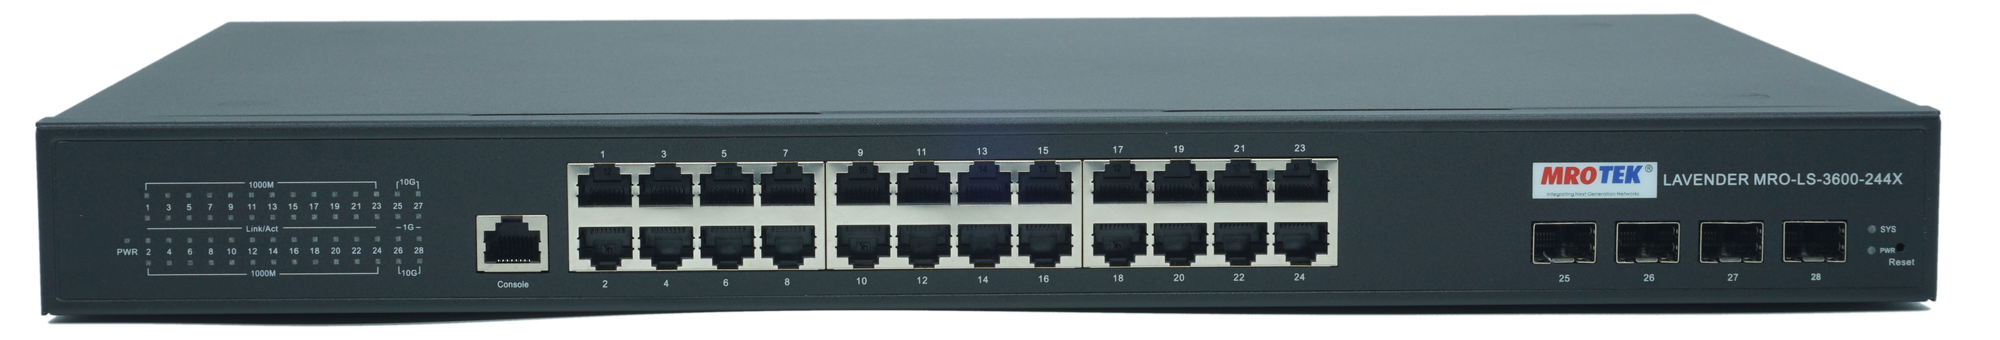
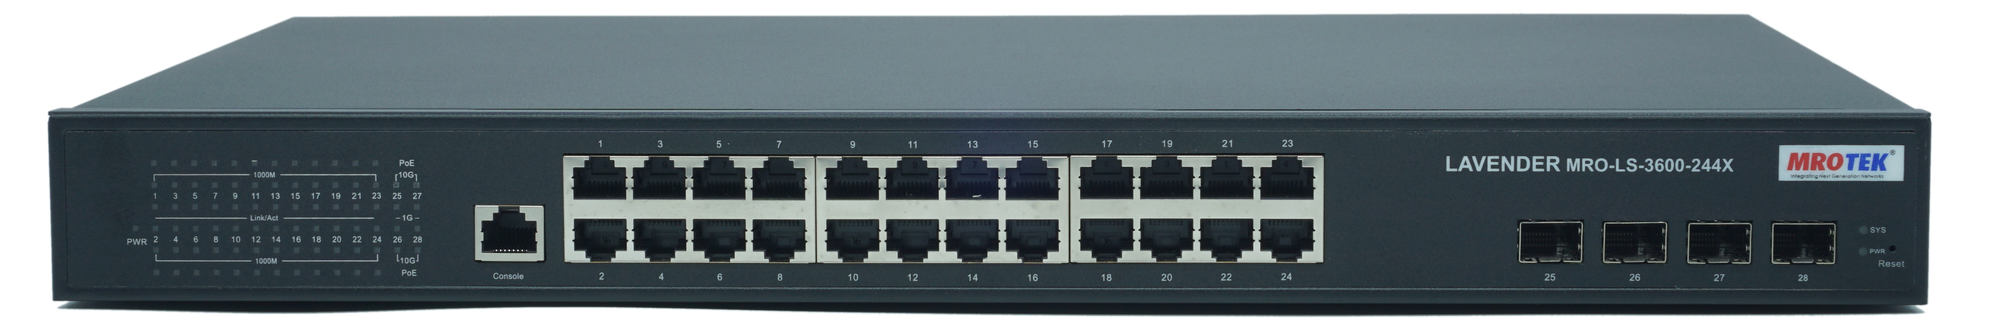
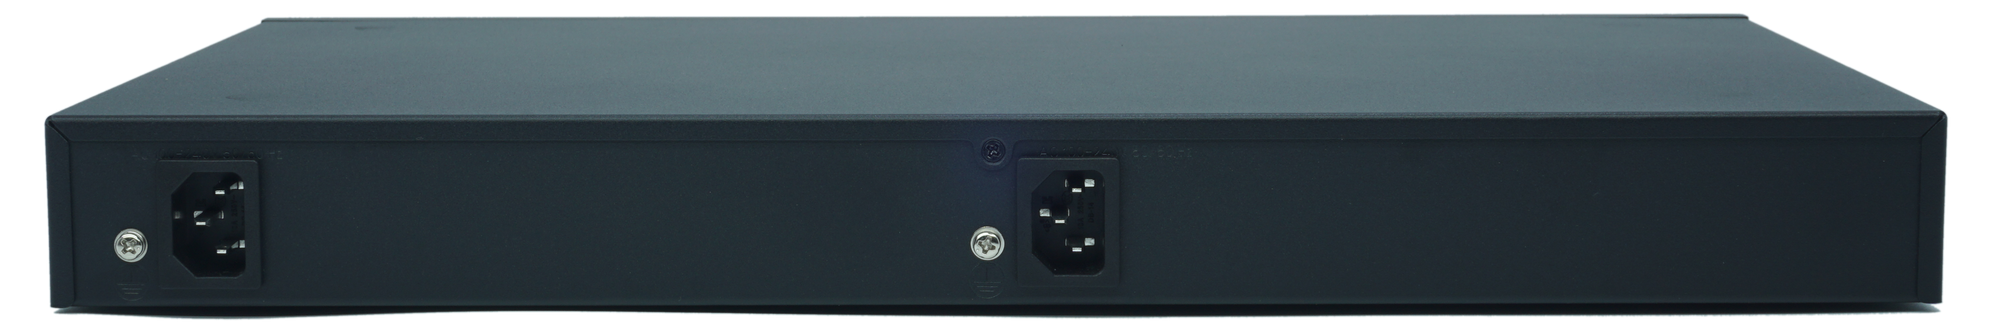
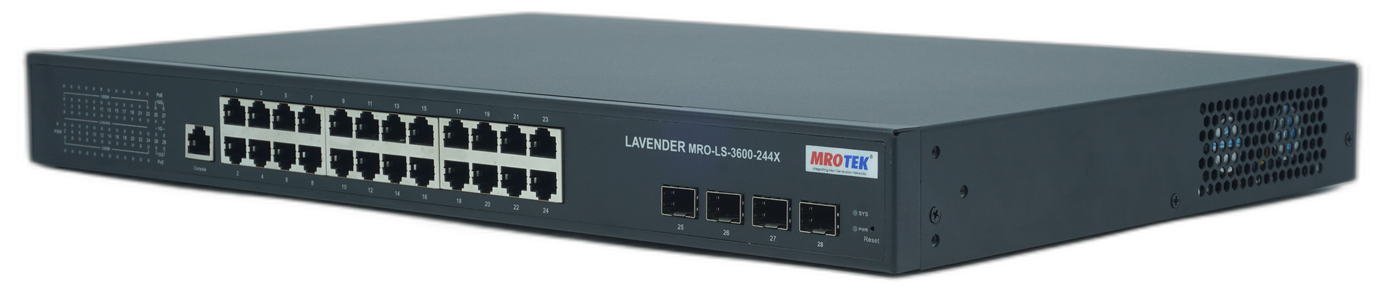
- 24/48× GE + 4× 1G/10G uplink slots
- Power options: AC, DC, PoE
- 1× RJ-45 console port
- 1U rack-mountable form factor
- Static Routing, RIP, OSPF, BGP, multiple OSPF processes
- URPF, ECMP, BFD
- PIM-SM, static multicast route
- Multicast receive control, illegal multicast source detection
- ARP Guard, local ARP proxy, proxy ARP, ARP binding
- Gratuitous ARP, ARP limit
- Anti ARP/NDP cheat, anti ARP/NDP scan
- DNS client, DNS relay
- ICMPv6, ND, DNSv6, VRRP
- MLD snooping, multicast VLAN
- MLD v1/v2, PIM-SM/DM, Anycast RP, ACL, QoS
- DHCP server/client, DHCP relay/option 82, DHCP snooping
- Port loopback detection, LLDP and LLDP-MED, UDLD
- IEEE 802.3ad LACP — up to 128 trunk groups, max 8 ports per trunk, LACP load balancing
- IGMP v1/v2/v3 snooping with L2 query, IGMP proxy, ND snooping, MLD v1/v2 snooping
- Flow control: HOL, IEEE 802.3x, bandwidth control
- MAC VLAN, voice VLAN, PVLAN, protocol VLAN, multicast VLAN, QinQ, selective QinQ, flexible QinQ
- 802.1D (STP), 802.1W (RSTP), 802.1S (MSTP), root guard, BPDU guard
- Humidity: 5%–90% non-condensing
- Operating temperature: 0°C to 50°C
- 802.1x AAA, port-based and MAC-based authentication
- Guest VLAN and auto VLAN
- RADIUS, TACACS+
- IP ACL, MAC ACL, IP-MAC ACL
- Standard and expanded ACL based on source/destination IP or MAC, IP protocol, TCP/UDP port, DSCP, ToS, IP precedence, VLAN, tag/untag, CoS
- Redirect and accounting-based ACL
- Rules configurable to port or VLAN
- Time-ranged ACL
- CLI, Web, Telnet, HTTPS/SSL, SSH v1/v2
- SNMP v1/v2c/v3, SNMP MIB, SNMP trap
- RMON groups 1, 2, 3, and 9
- Syslog and external syslog server
- FTP, NTP, RADIUS, TACACS
- 8 queues — SWRR, SP, WRR, WDRR, SWDRR scheduling
- Traffic classification based on 802.1p CoS, ToS, DiffServ DSCP, ACL, port number
- Traffic policing, priority mark/remark
- LAVENDER MRO-LS-3600-244X — Managed L3 Switch, 24× GE + 4× 1G/10G uplink slots, Power AC, PoE (option)
- LAVENDER MRO-LS-3600-84X — Managed L3 Switch, 8× GE + 4× 1G/10G uplink slots, Power AC
- LAVENDER MRO-LS-3600-486X — Managed L3 Switch, 48× GE + 6× 1G/10G uplink slots, AC Power
- LAVENDER MRO-LS-3600-24F4X — Managed L3 Switch, 24× 1G Fiber + 4× 1G/10G uplink slots, AC Power
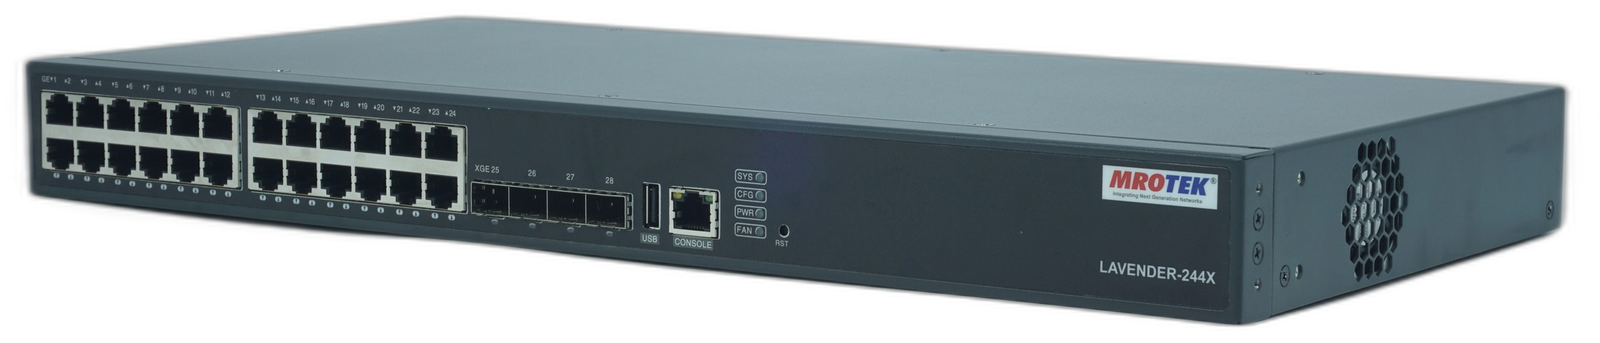
- 24× 10/100/1000M RJ45 Ethernet ports
- 4× 1G/10G uplink slots
- 1× RJ-45 console port
- 1× USB port for configuration backup/restore
- 1U rack-mountable form factor
- 128 Gbps non-blocking switching capacity
- 95.3 Mpps forwarding rate
- 16K MAC address table (static and dynamic)
- IEEE 802.1Q VLAN — up to 4094 VLANs
- 9K jumbo frame support
- Store-and-forward switching with CRC error detection
- Static route support for network connectivity
- Dynamic routing protocols — RIP and OSPF — for campus and enterprise networks
- IEEE 802.1Q VLAN, QinQ (802.1ad), voice VLAN, private VLAN
- IEEE 802.3ad LACP link aggregation
- Spanning Tree: 802.1D (STP), 802.1W (RSTP), 802.1S (MSTP), BPDU, root guard
- IGMP v1/v2/v3, IGMP Snooping, IGMP Fast Leave
- MAC address VLAN binding
- 10G Ether-ring (ERPS ring protection for backbone redundancy)
- Storm control for broadcast, multicast, and unknown unicast
- IEEE 802.1x port-based and MAC-based authentication
- RADIUS and TACACS+ authentication
- Port isolation and port security
- ACL — policy control by VLAN ID, source MAC/IP address, and protocol port
- IP Source Guard and IP MAC port binding
- Flow classification based on L2/L3/L4 protocols
- 802.1P/DSCP priority marking
- SP, WRR, and SP+WRR scheduling
- Congestion avoidance with Tail-Drop and WRED
- Web-based GUI with dashboard and port monitoring
- CLI via console, Telnet, SSH v2
- SNMP v1/v2c/v3 with RMON
- Dual firmware image for resilient upgrades
- SNTP/NTP time synchronization
- Managed via OmniEye NMS/EMS
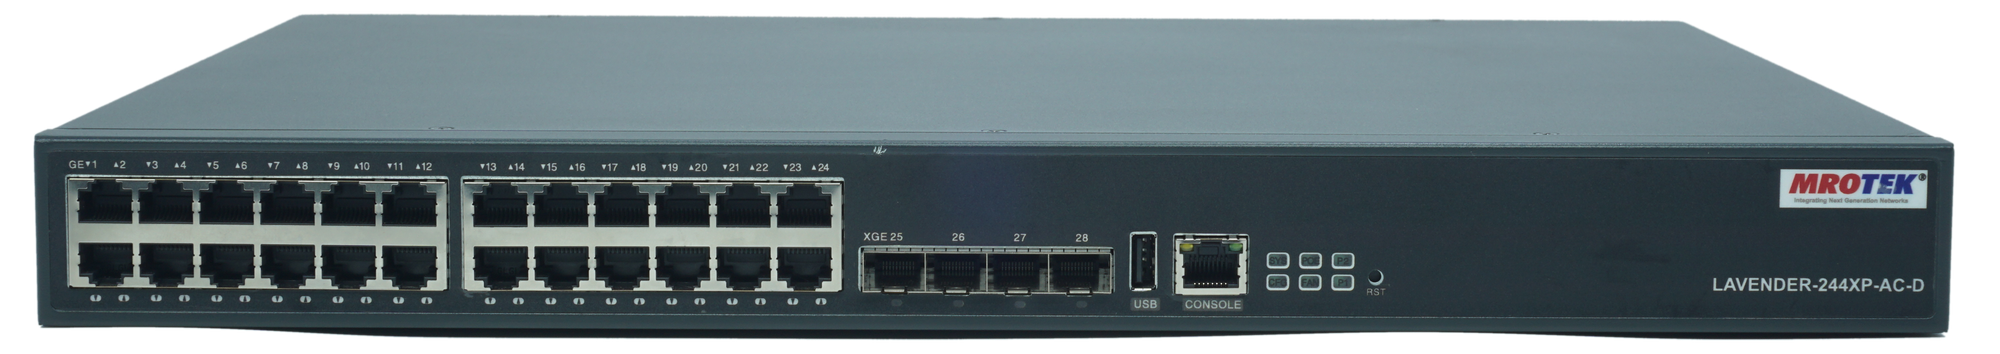
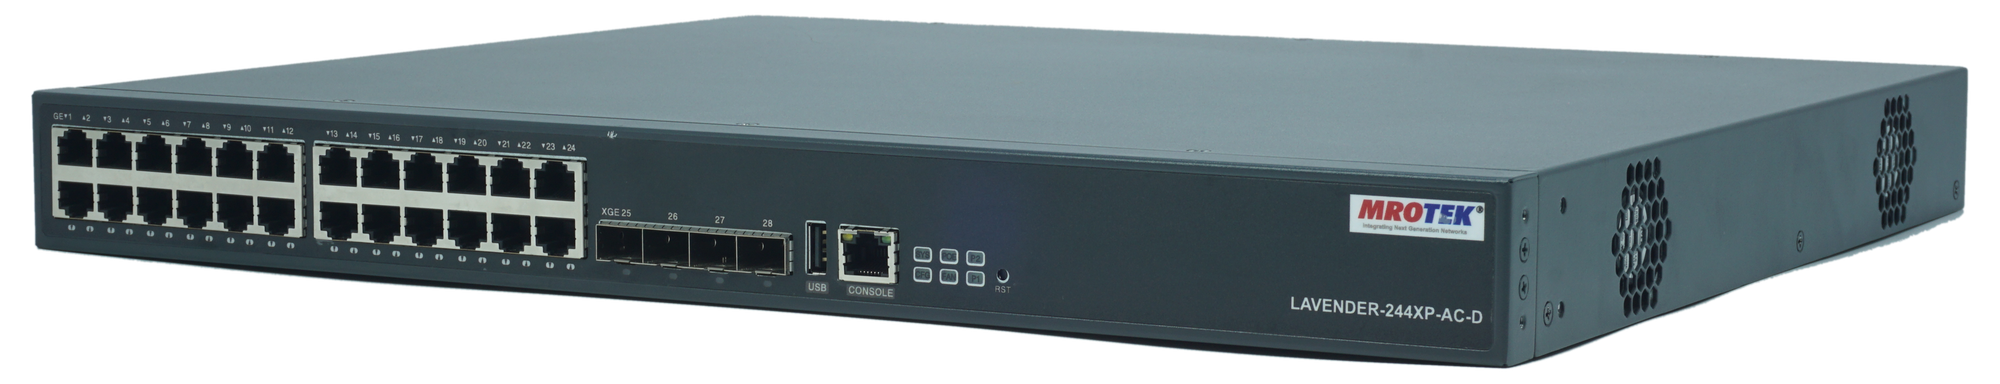
- 24× 10/100/1000M RJ45 PoE+ Ethernet ports (IEEE 802.3af/at)
- 4× 1G/10G uplink slots
- 1× RJ-45 console port
- 1× USB port for configuration backup/restore
- 1U rack-mountable form factor
- IEEE 802.3af (PoE) — up to 15.4W per port
- IEEE 802.3at (PoE+) — up to 30W per port
- 24 PoE+ ports — all access ports PoE capable
- 370W total PoE power budget
- Intelligent PoE budget management with per-port priority
- 128 Gbps non-blocking switching capacity
- 95.3 Mpps forwarding rate
- 16K MAC address table (static and dynamic)
- IEEE 802.1Q VLAN — up to 4094 VLANs
- 9K jumbo frame support
- Store-and-forward switching with CRC error detection
- Static route support for network connectivity
- Dynamic routing protocols — RIP and OSPF — for campus and enterprise networks
- IEEE 802.1Q VLAN, QinQ (802.1ad), voice VLAN, private VLAN
- IEEE 802.3ad LACP link aggregation
- Spanning Tree: 802.1D (STP), 802.1W (RSTP), 802.1S (MSTP), BPDU, root guard
- IGMP v1/v2/v3, IGMP Snooping, IGMP Fast Leave
- MAC address VLAN binding
- 10G Ether-ring (ERPS ring protection for backbone redundancy)
- Storm control for broadcast, multicast, and unknown unicast
- IEEE 802.1x port-based and MAC-based authentication
- RADIUS and TACACS+ authentication
- Port isolation and port security
- ACL — policy control by VLAN ID, source MAC/IP address, and protocol port
- IP Source Guard and IP MAC port binding
- Flow classification based on L2/L3/L4 protocols
- 802.1P/DSCP priority marking
- SP, WRR, and SP+WRR scheduling
- Congestion avoidance with Tail-Drop and WRED
- Web-based GUI with PoE monitoring dashboard
- CLI via console, Telnet, SSH v2
- SNMP v1/v2c/v3 with RMON
- Dual firmware image for resilient upgrades
- SNTP/NTP time synchronization
- Managed via OmniEye NMS/EMS
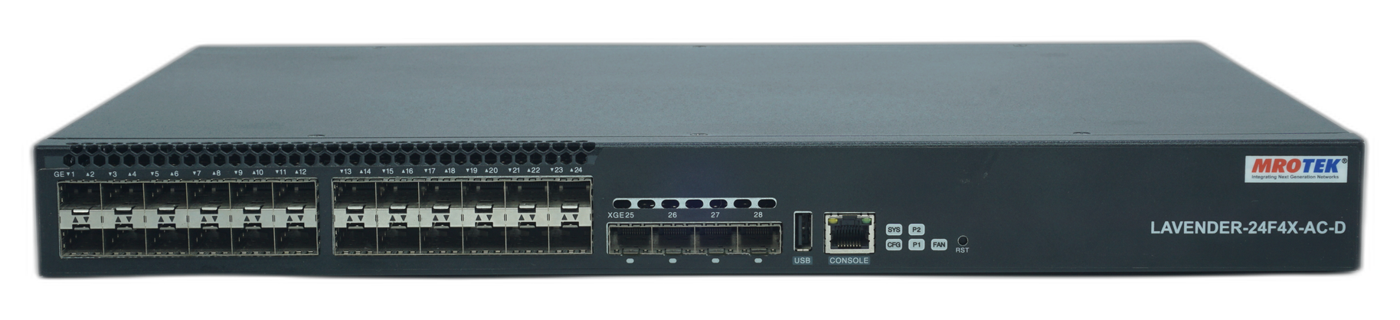
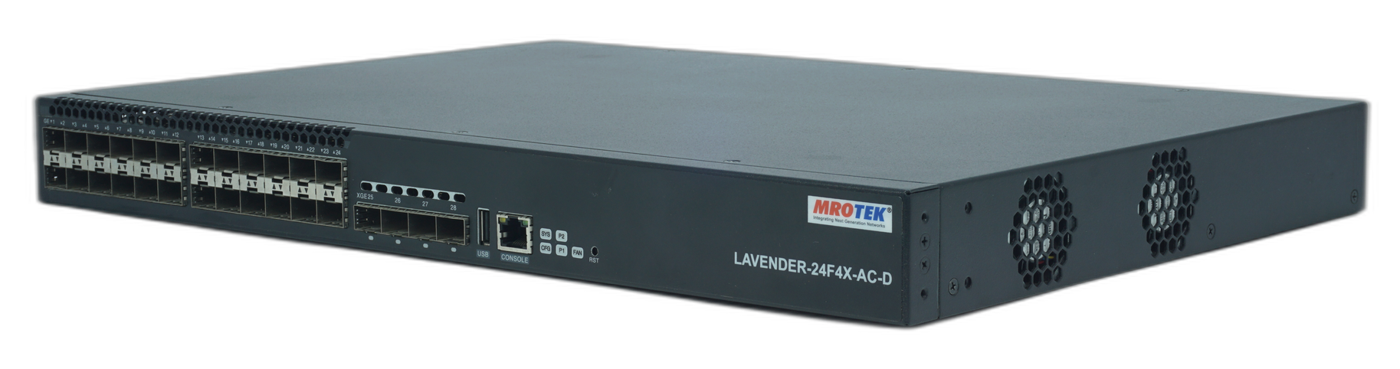
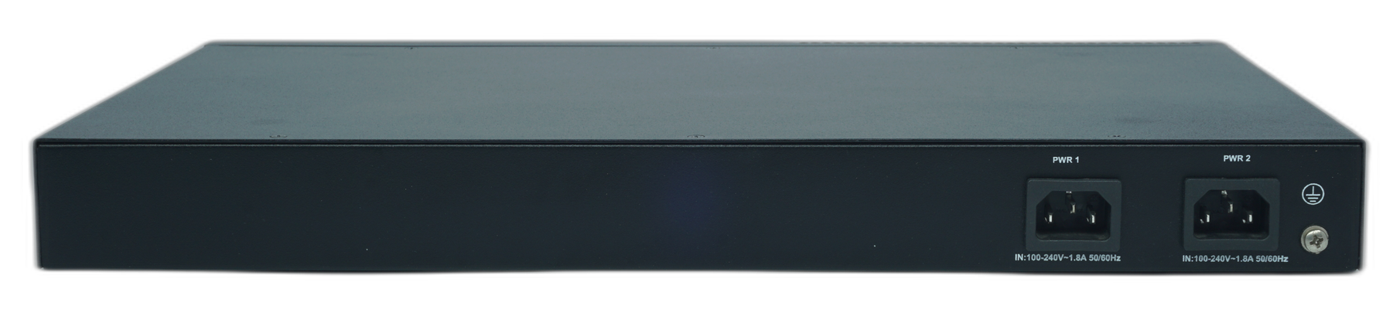
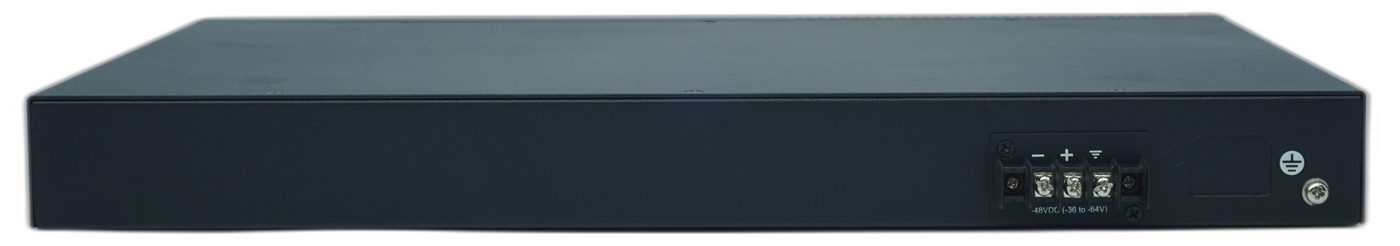
- 24× 1G fibre access ports
- 4× 1G/10G uplink slots
- 1× RJ-45 console port
- 1U rack-mountable form factor
- 128 Gbps non-blocking switching capacity
- 95.3 Mpps forwarding rate
- 16K MAC address table (static and dynamic)
- 4K VLAN, QinQ (802.1ad), private VLAN
- Stackable
- Static route support for network connectivity
- Dynamic routing protocols — RIP and OSPF — for campus and enterprise networks
- 16K MAC table with static and dynamic MAC addresses, plus MAC address VLAN binding
- IGMP v1/v2/v3, IGMP Snooping, IGMP Fast Leave, LACP for link aggregation
- 4K VLAN, QinQ, private VLAN
- ERPS for ring architecture
- ACL — policy control by VLAN ID, source MAC/IP address, and protocol port
- Storm control for broadcast, multicast, and unicast
- Port isolation and port security
- IP Source Guard and IP MAC port binding
- Authentication — IEEE 802.1x, RADIUS and TACACS+
- Flow classification based on L2/L3/L4 protocols
- 802.1P/DSCP priority marking
- SP, WRR, and SP+WRR scheduling
- Congestion avoidance with Tail-Drop and WRED
- Console, Telnet, SSH2.0, and Web GUI management
- SNMP v1/v2/v3 with TFTP and RMON
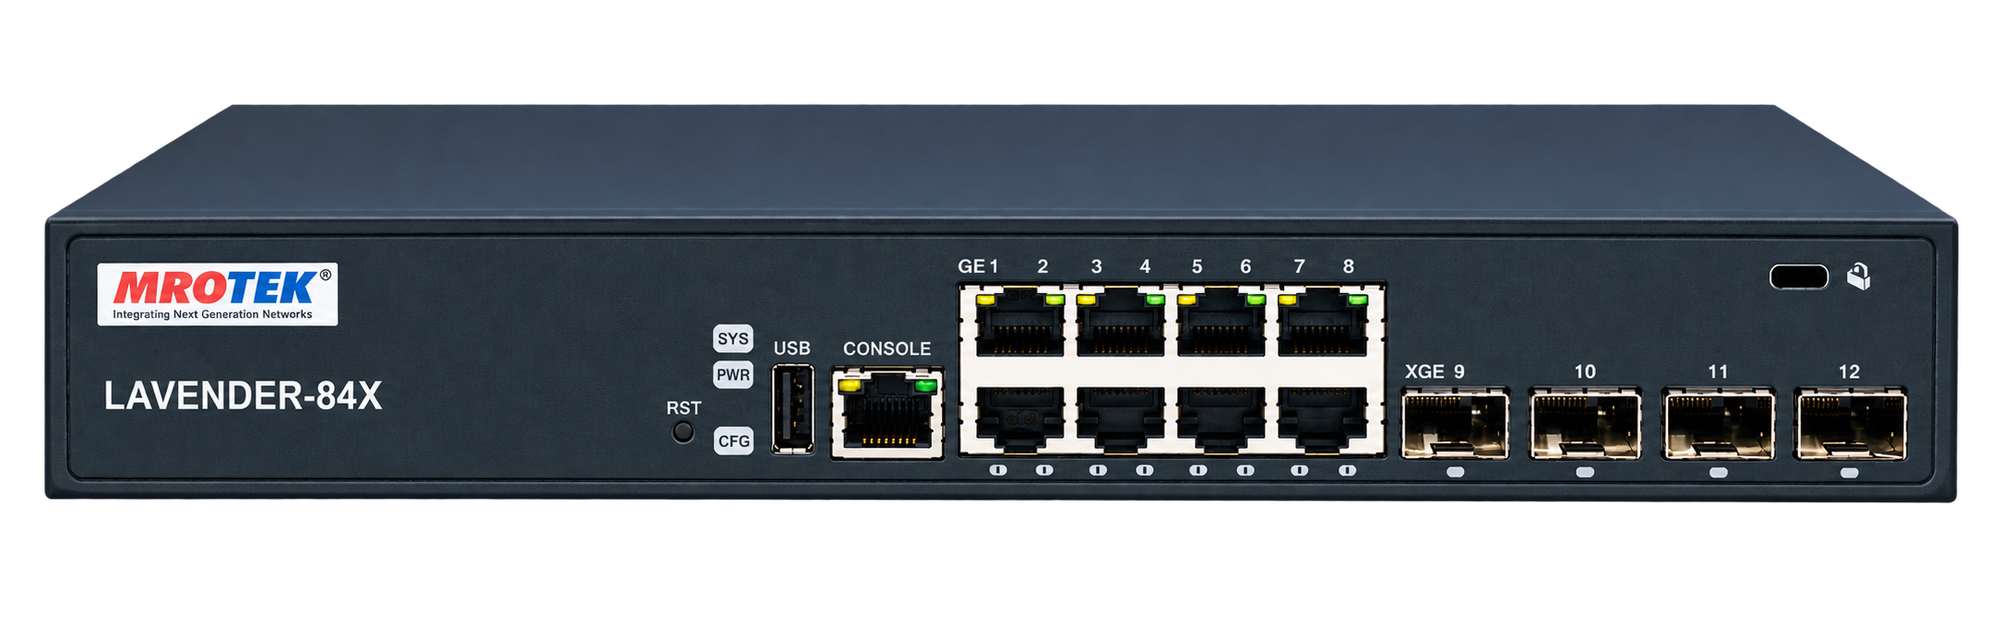
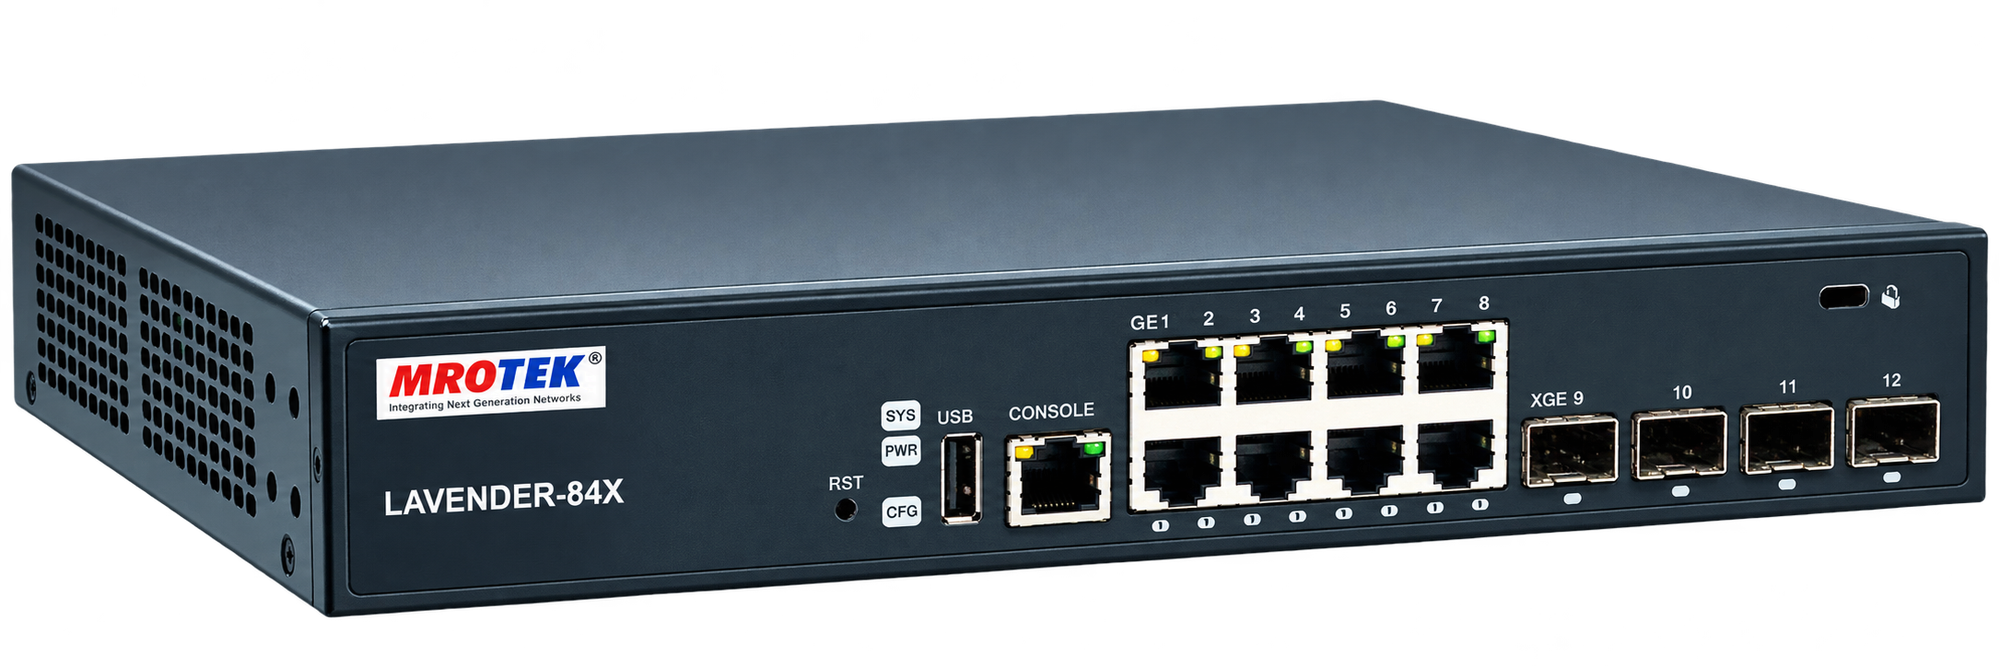
- 8× 10/100/1000M RJ45 Ethernet ports
- 4× 1G/10G uplink slots
- 1× RJ-45 console port
- 1× USB port for configuration backup/restore
- Compact 1U rack-mountable or desktop form factor
- 96 Gbps non-blocking switching capacity
- 71.42 Mpps forwarding rate
- 16K MAC address table (static and dynamic)
- IEEE 802.1Q VLAN — up to 4094 VLANs
- 9K jumbo frame support
- Store-and-forward switching with CRC error detection
- Static route support for network connectivity
- Dynamic routing protocols — RIP and OSPF — for campus and enterprise networks
- IEEE 802.1Q VLAN, QinQ (802.1ad), voice VLAN, private VLAN
- IEEE 802.3ad LACP link aggregation
- Spanning Tree: 802.1D (STP), 802.1W (RSTP), 802.1S (MSTP), BPDU, root guard
- IGMP v1/v2/v3, IGMP Snooping, IGMP Fast Leave
- MAC address VLAN binding
- 10G Ether-ring (ERPS ring protection for backbone redundancy)
- Storm control for broadcast, multicast, and unknown unicast
- IEEE 802.1x port-based and MAC-based authentication
- RADIUS and TACACS+ authentication
- Port isolation and port security
- ACL — policy control by VLAN ID, source MAC/IP address, and protocol port
- IP Source Guard and IP MAC port binding
- Flow classification based on L2/L3/L4 protocols
- 802.1P/DSCP priority marking
- SP, WRR, and SP+WRR scheduling
- Congestion avoidance with Tail-Drop and WRED
- Web-based GUI with dashboard and port monitoring
- CLI via console, Telnet, SSH v2
- SNMP v1/v2c/v3 with RMON
- Dual firmware image for resilient upgrades
- SNTP/NTP time synchronization
- Managed via OmniEye NMS/EMS
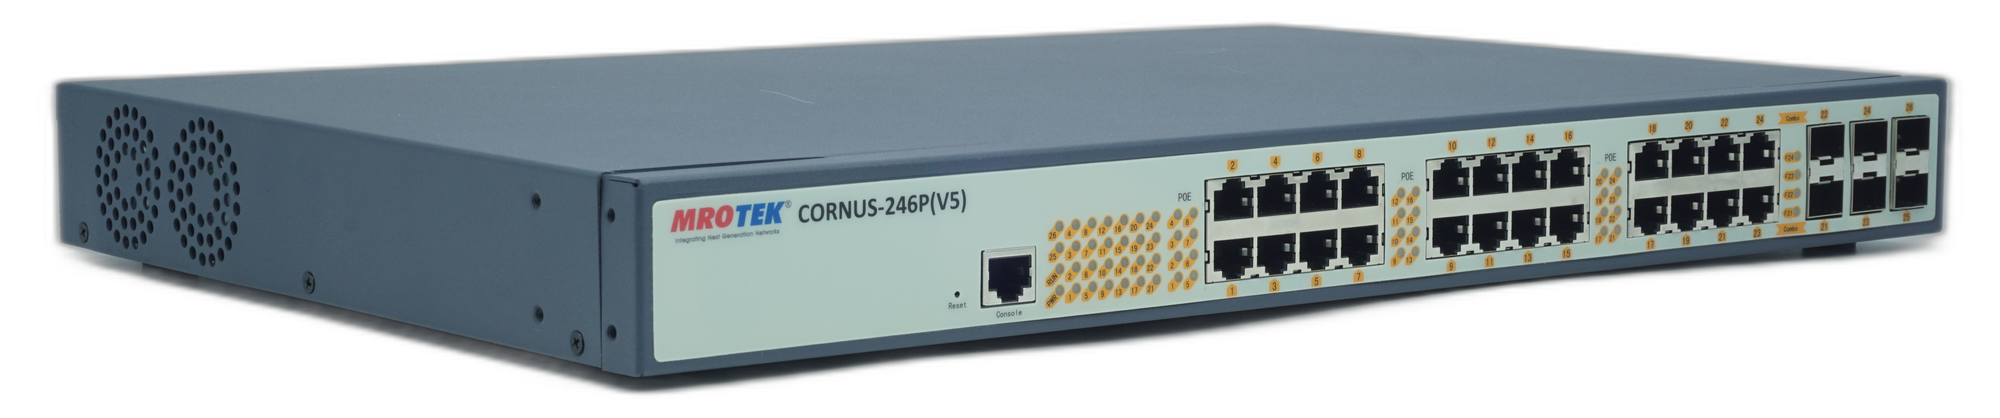
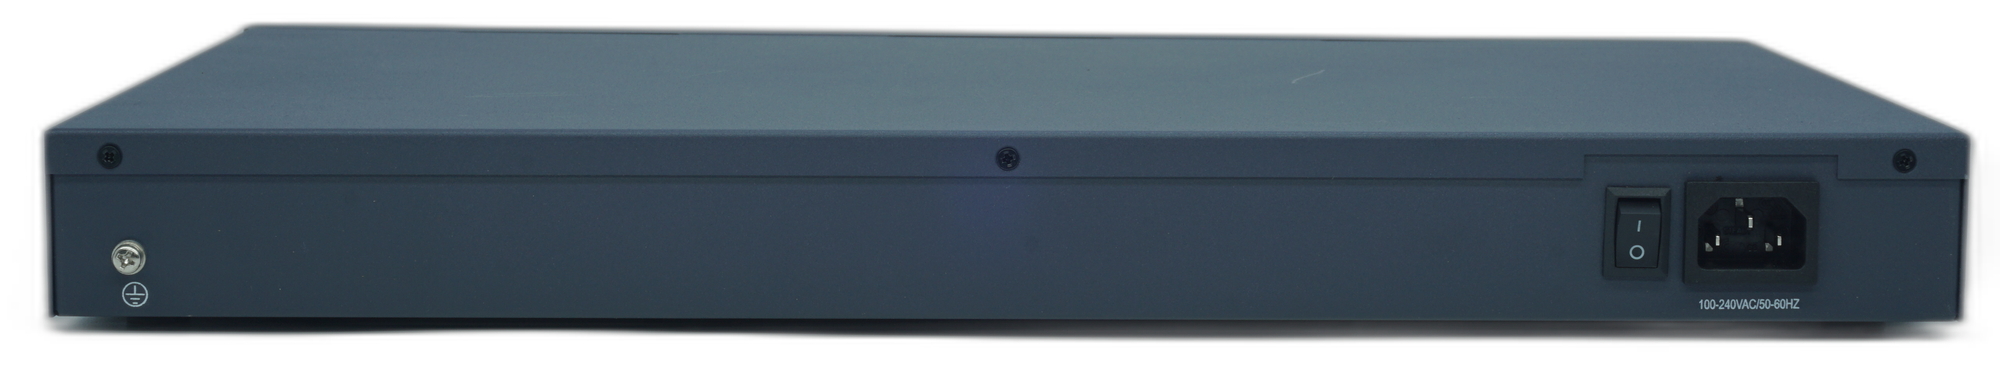
- 24× 10/100/1000M RJ45 PoE+ Ethernet ports (IEEE 802.3af/at)
- 4× 1G fibre uplink ports
- 1× RJ-45 console port
- 1RU form factor
- IEEE 802.3af (PoE) — up to 15.4W per port
- IEEE 802.3at (PoE+) — up to 30W per port
- 24× PoE+ ports — all access ports PoE capable
- PoE budget: 300-450W total
- 53 Gbps non-blocking switching capacity
- 38 Mpps forwarding rate
- 8K MAC address table (static and dynamic)
- IEEE 802.1Q VLAN — up to 4094 VLANs
- Store-and-forward switching
- IEEE 802.1Q VLAN, QinQ (802.1ad), private VLAN
- IEEE 802.3ad LACP link aggregation with port mirroring
- Spanning Tree: STP (802.1D), RSTP (802.1w), MSTP (802.1s) with BPDU guard and root guard
- IGMP snooping v1/v2/v3 for multicast traffic
- ITU-T G.8031/G.8032 ERPS Ethernet ring protection switching
- ACL — policy-based control by VLAN ID, source MAC/IP address, and protocol port
- Storm control for broadcast, multicast, and unicast traffic
- Port security with MAC address binding
- IP-MAC port binding
- IEEE 802.1x port-based authentication
- RADIUS and TACACS+ authentication
- IEEE 802.1p class of service (CoS)
- IP DSCP-based CoS
- Fragment and DSCP-based traffic classification
- Console, Telnet, SSH v2, Web GUI management
- SNMP v1/v2c/v3 with RMON
- Firmware image upgrade
- Managed via OmniEye NMS/EMS (optional)
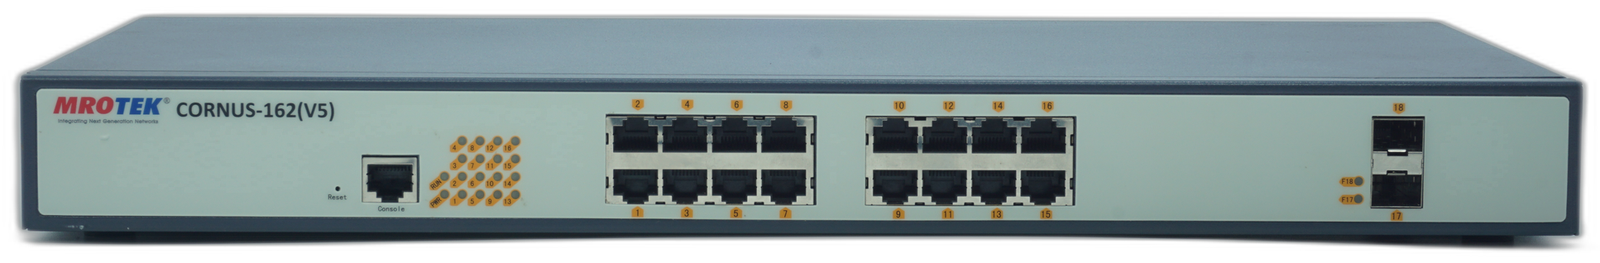
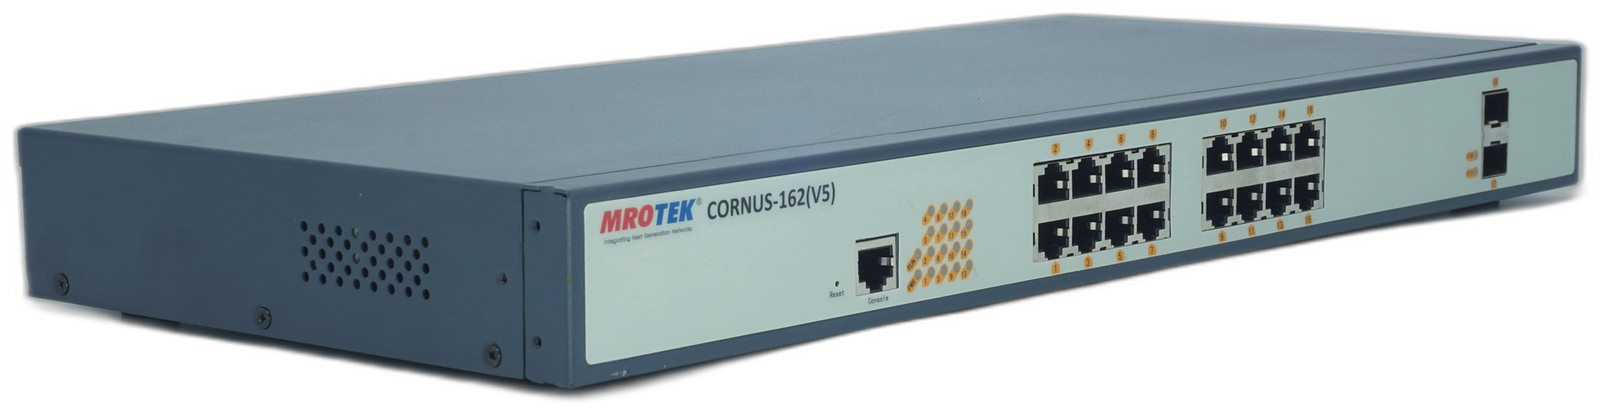
- 16× 10/100/1000M RJ45 PoE+ Ethernet ports (IEEE 802.3af/at)
- 2× 1G fibre uplink ports
- 1× RJ-45 console port
- 1RU form factor
- IEEE 802.3af (PoE) — up to 15.4W per port
- IEEE 802.3at (PoE+) — up to 30W per port
- 16× PoE+ ports — all access ports PoE capable
- PoE budget: 250W total
- 36 Gbps non-blocking switching capacity
- 26.784 Mpps forwarding rate
- 8K MAC address table (static and dynamic)
- IEEE 802.1Q VLAN — up to 4094 VLANs
- Store-and-forward switching
- IEEE 802.1Q VLAN, QinQ (802.1ad), private VLAN
- IEEE 802.3ad LACP link aggregation with port mirroring
- Spanning Tree: STP (802.1D), RSTP (802.1w), MSTP (802.1s) with BPDU guard and root guard
- IGMP snooping v1/v2/v3 for multicast traffic
- ITU-T G.8031/G.8032 ERPS Ethernet ring protection switching
- ACL — policy-based control by VLAN ID, source MAC/IP address, and protocol port
- Storm control for broadcast, multicast, and unicast traffic
- Port security with MAC address binding
- IP-MAC port binding
- IEEE 802.1x port-based authentication
- RADIUS and TACACS+ authentication
- IEEE 802.1p class of service (CoS)
- IP DSCP-based CoS
- Fragment and DSCP-based traffic classification
- Console, Telnet, SSH v2, Web GUI management
- SNMP v1/v2c/v3 with RMON
- Firmware image upgrade
- Managed via OmniEye NMS/EMS (optional)
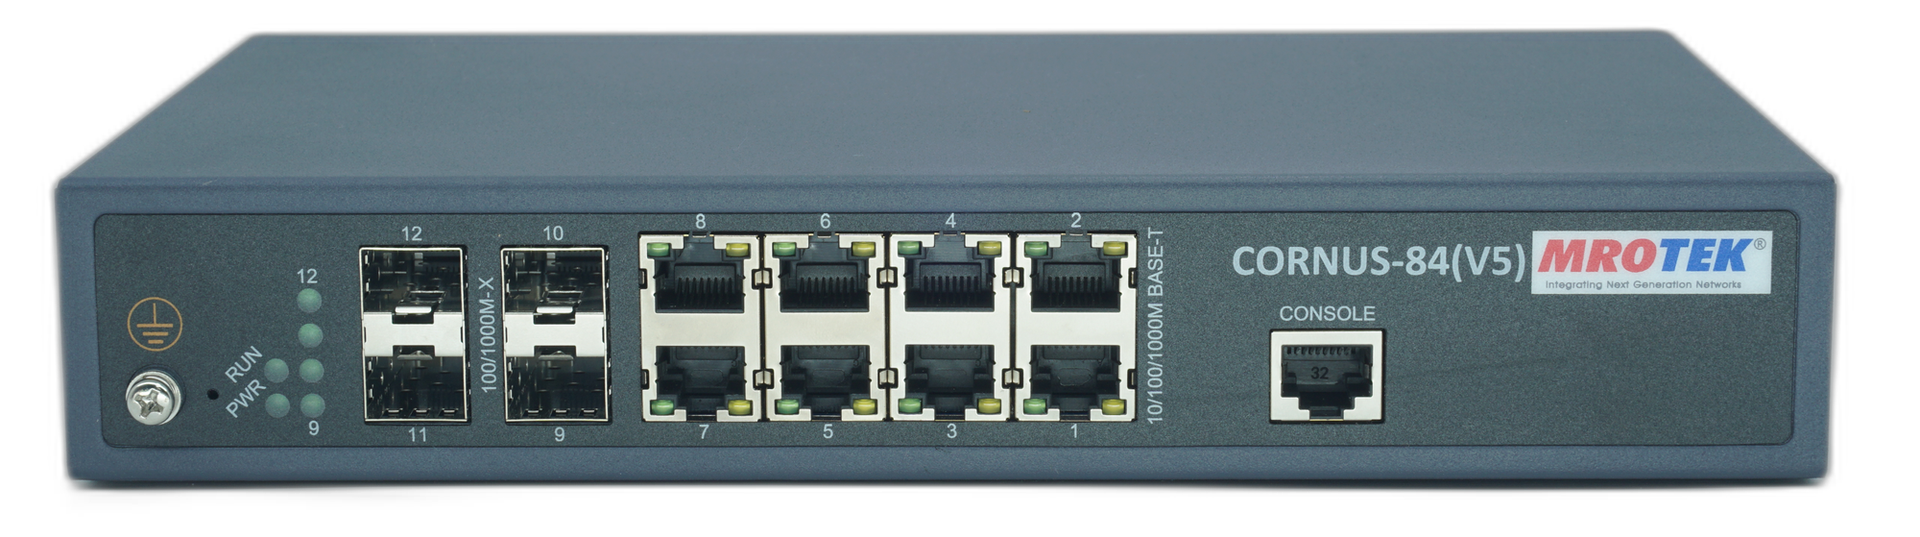
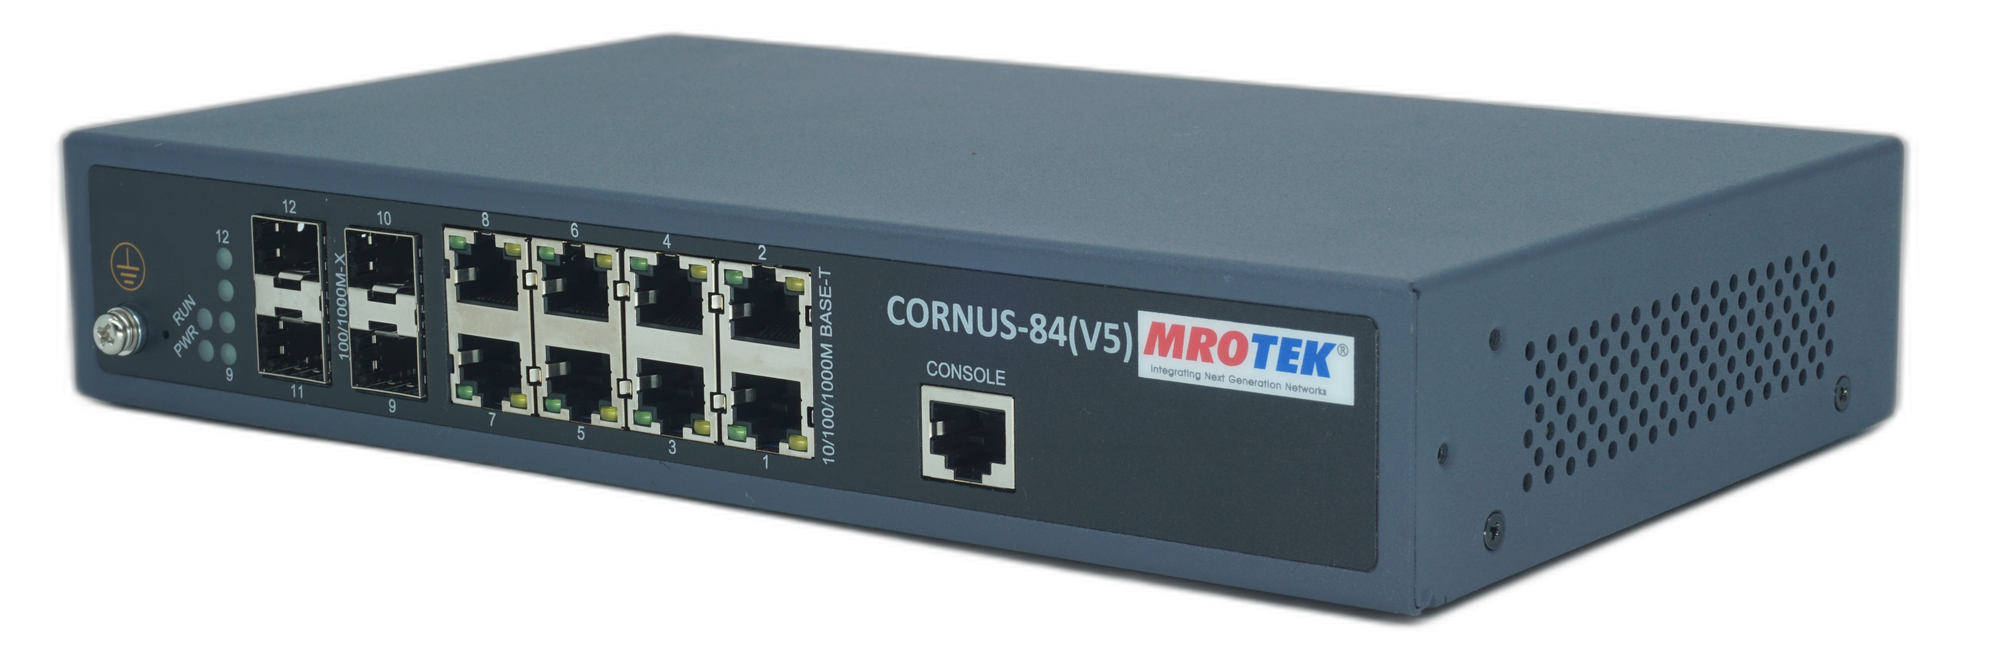
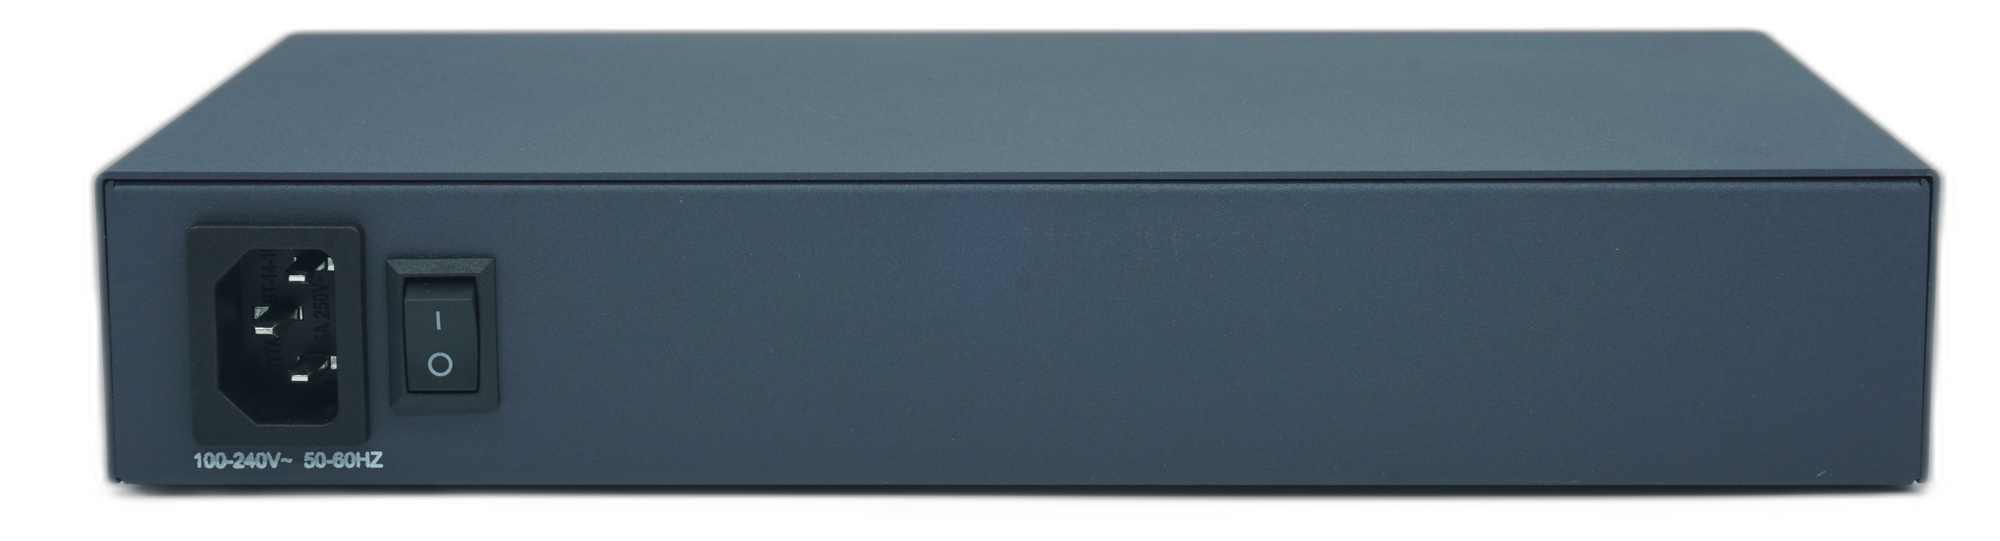
- 8× 10/100/1000M RJ45 Ethernet ports
- 4× 1G fibre uplink ports
- 1× RJ-45 console port
- 19-inch rack-mountable, 1RU form factor
- Power supply — single AC/DC configurations
- 24 Gbps non-blocking switching capacity
- 17.9 Mpps forwarding rate
- 8K MAC address table (static and dynamic)
- IEEE 802.1Q VLAN — up to 4094 VLANs
- Store-and-forward switching
- IEEE 802.1Q VLAN, QinQ (802.1ad), private VLAN
- IEEE 802.3ad LACP link aggregation with port mirroring
- Spanning Tree: STP (802.1D), RSTP (802.1w), MSTP (802.1s) with BPDU guard and root guard
- IGMP snooping v1/v2/v3 for multicast traffic
- ITU-T G.8031/G.8032 ERPS Ethernet ring protection switching
- ACL — policy-based control by VLAN ID, source MAC/IP address, and protocol port
- Storm control for broadcast, multicast, and unicast traffic
- Port security with MAC address binding
- IP-MAC port binding
- IEEE 802.1x port-based authentication
- RADIUS and TACACS+ authentication
- IEEE 802.1p class of service (CoS)
- IP DSCP-based CoS
- Fragment and DSCP-based traffic classification
- Console, Telnet, SSH v2, Web GUI management
- SNMP v1/v2c/v3 with RMON
- Firmware image upgrade
- Managed via OmniEye NMS/EMS (optional)
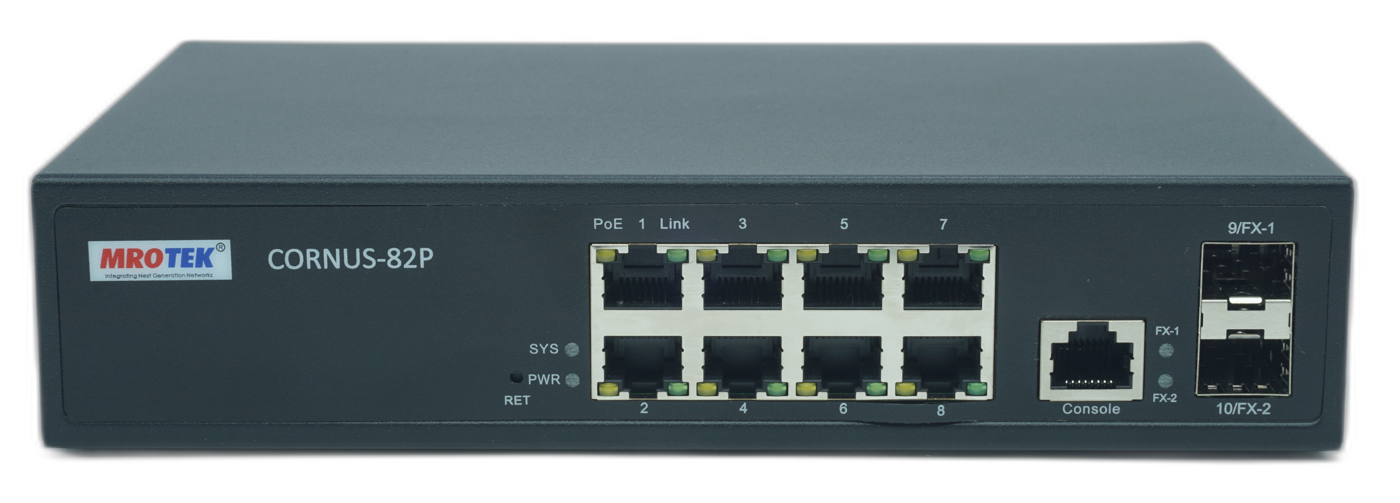
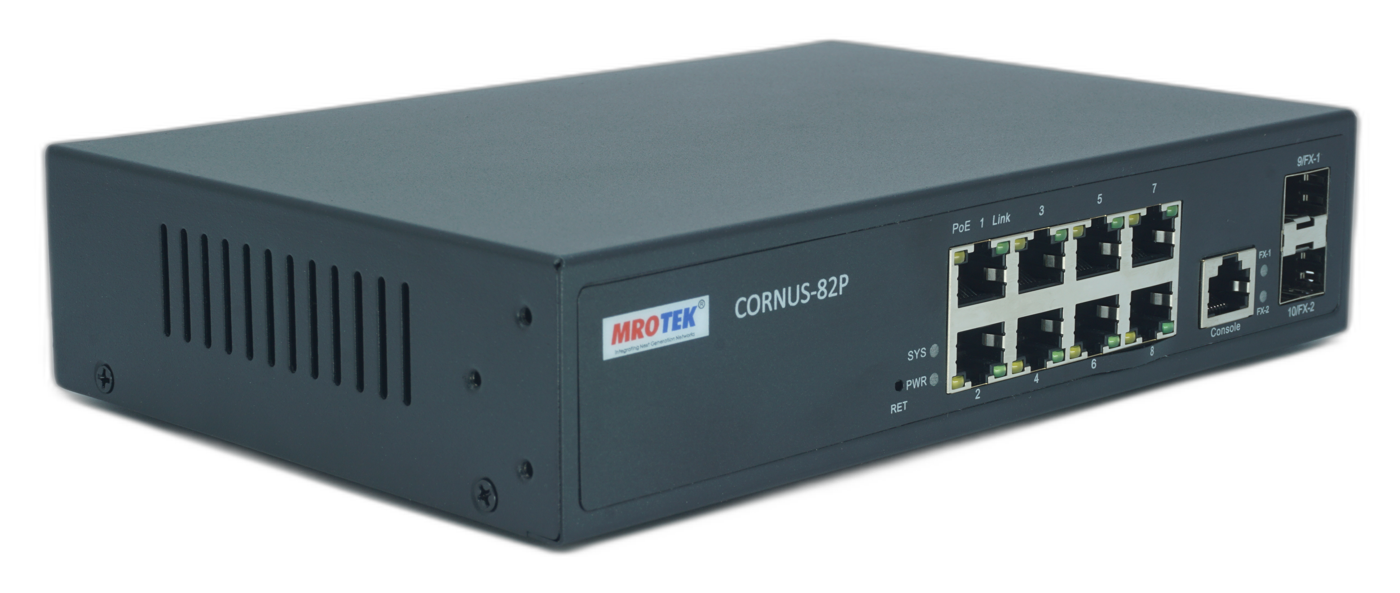
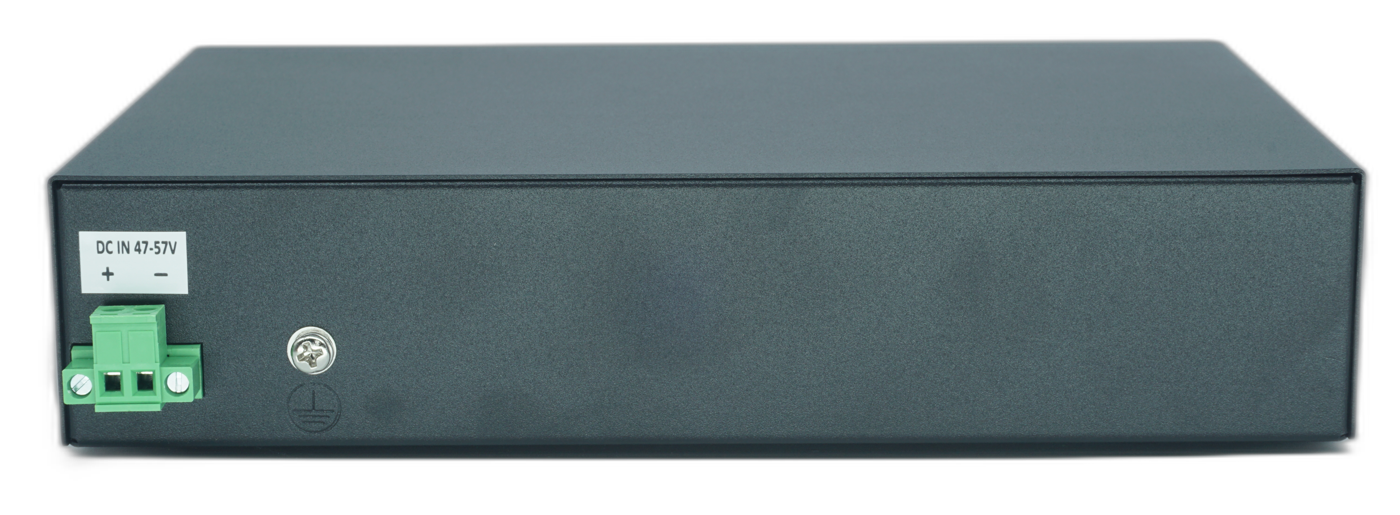
- 8× 10/100/1000M RJ45 PoE+ Ethernet ports (IEEE 802.3af/at)
- 2× 1G fibre uplink ports
- 1× RJ-45 console port
- 19-inch rack-mountable, 1RU form factor
- Power supply — single AC/DC or dual AC+DC/AC+AC configurations
- IEEE 802.3af (PoE) — up to 15.4W per port
- IEEE 802.3at (PoE+) — up to 30W per port
- 8× PoE+ ports — all access ports PoE capable
- PoE budget: 120W total
- 20 Gbps non-blocking switching capacity
- 14.88 Mpps forwarding rate
- 8K MAC address table (static and dynamic)
- IEEE 802.1Q VLAN — up to 4094 VLANs
- Store-and-forward switching
- IEEE 802.1Q VLAN, QinQ (802.1ad), private VLAN
- IEEE 802.3ad LACP link aggregation with port mirroring
- Spanning Tree: STP (802.1D), RSTP (802.1w), MSTP (802.1s) with BPDU guard and root guard
- IGMP snooping v1/v2/v3 for multicast traffic
- ITU-T G.8031/G.8032 ERPS Ethernet ring protection switching
- ACL — policy-based control by VLAN ID, source MAC/IP address, and protocol port
- Storm control for broadcast, multicast, and unicast traffic
- Port security with MAC address binding
- IP-MAC port binding
- IEEE 802.1x port-based authentication
- RADIUS and TACACS+ authentication
- IEEE 802.1p class of service (CoS)
- IP DSCP-based CoS
- Fragment and DSCP-based traffic classification
- Console, Telnet, SSH v2, Web GUI management
- SNMP v1/v2c/v3 with RMON
- Firmware image upgrade
- Managed via OmniEye NMS/EMS (optional)
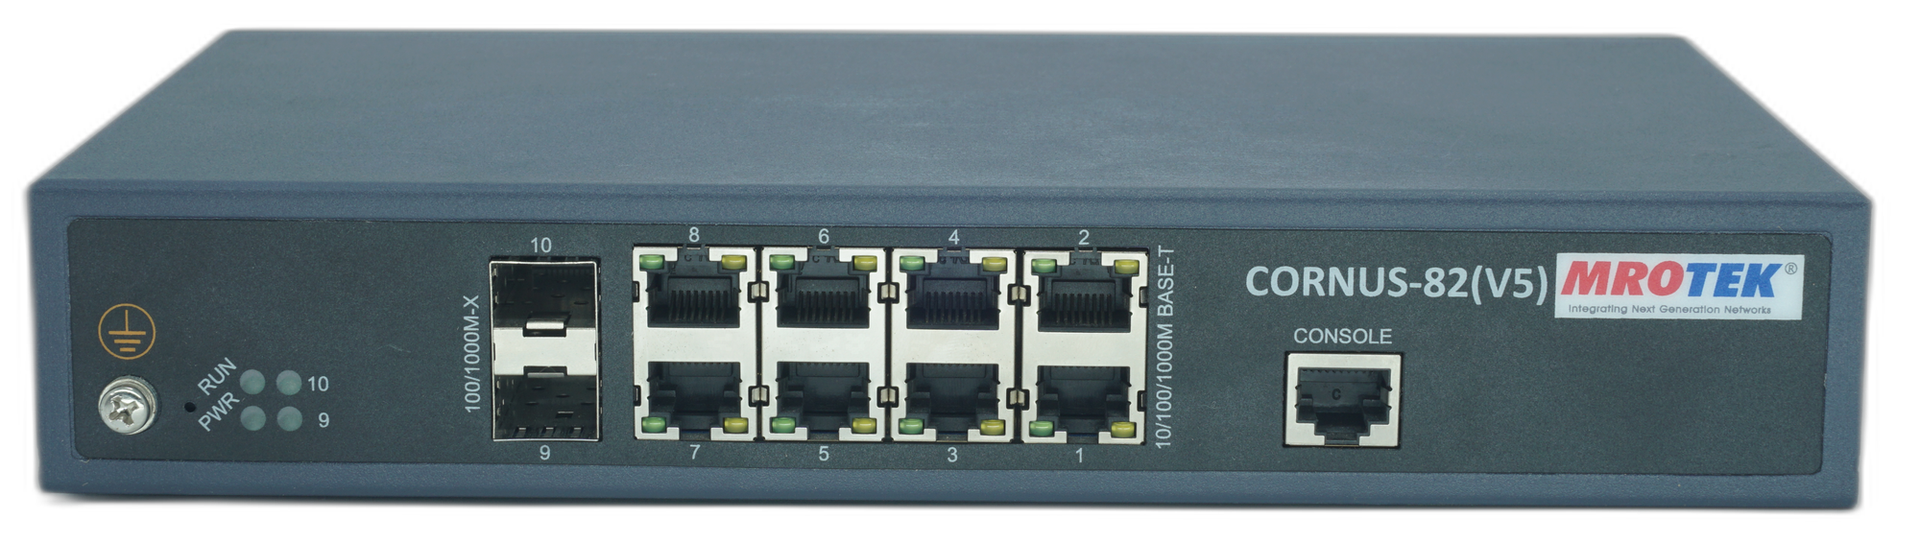
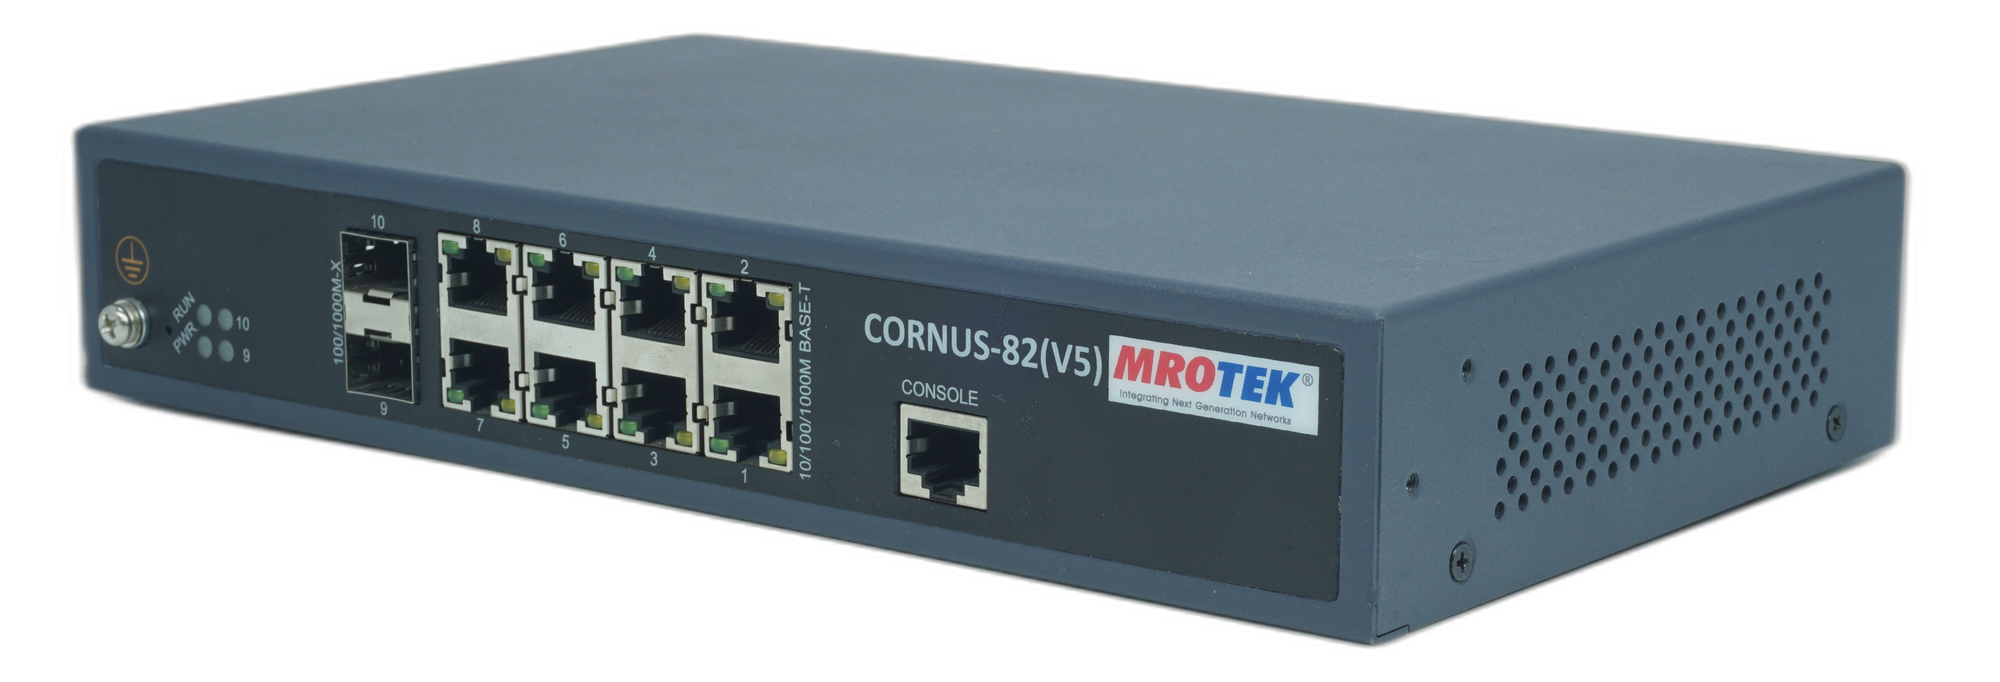
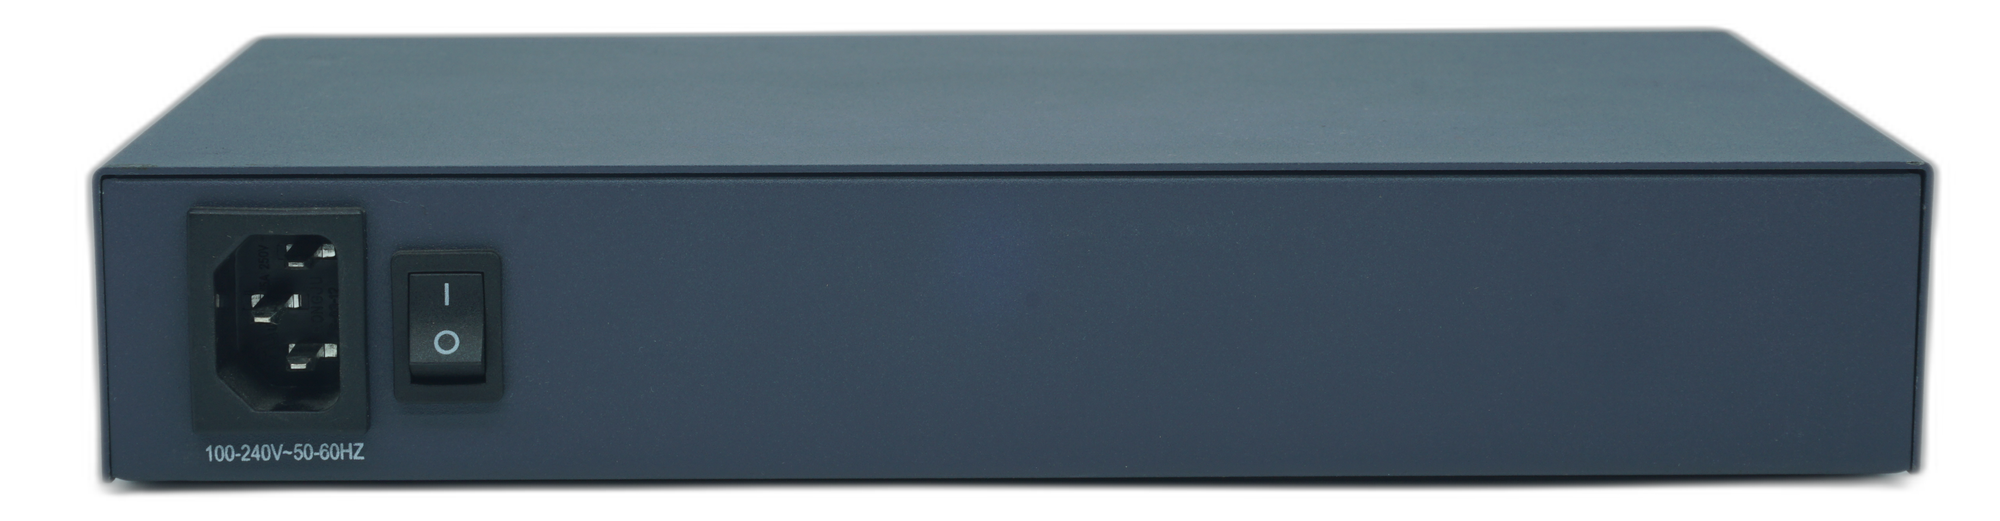
- 8× 10/100/1000M RJ45 Ethernet ports
- 2× 1G fibre uplink ports
- 1× RJ-45 console port
- 19-inch rack-mountable, 1RU form factor
- 20 Gbps non-blocking switching capacity
- 14.88 Mpps forwarding rate
- 8K MAC address table (static and dynamic)
- IEEE 802.1Q VLAN — up to 4094 VLANs
- Store-and-forward switching
- IEEE 802.1Q VLAN, QinQ (802.1ad), private VLAN
- IEEE 802.3ad LACP link aggregation with port mirroring
- Spanning Tree: STP (802.1D), RSTP (802.1w), MSTP (802.1s) with BPDU guard and root guard
- IGMP snooping v1/v2/v3 for multicast traffic
- ITU-T G.8031/G.8032 ERPS Ethernet ring protection switching
- ACL — policy-based control by VLAN ID, source MAC/IP address, and protocol port
- Storm control for broadcast, multicast, and unicast traffic
- Port security with MAC address binding
- IP-MAC port binding
- IEEE 802.1x port-based authentication
- RADIUS and TACACS+ authentication
- IEEE 802.1p class of service (CoS)
- IP DSCP-based CoS
- Fragment and DSCP-based traffic classification
- Console, Telnet, SSH v2, Web GUI management
- SNMP v1/v2c/v3 with RMON
- Firmware image upgrade
- Managed via OmniEye NMS/EMS (optional)
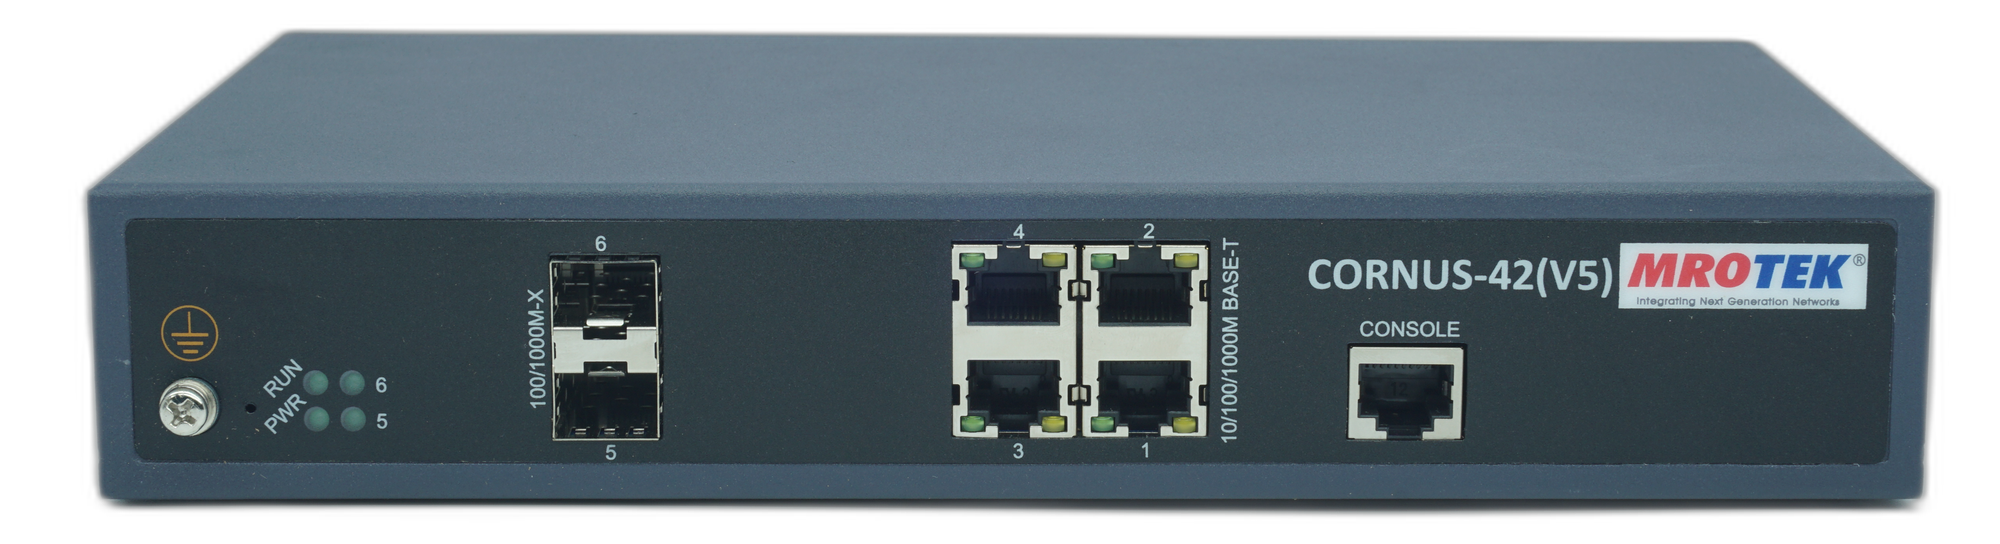
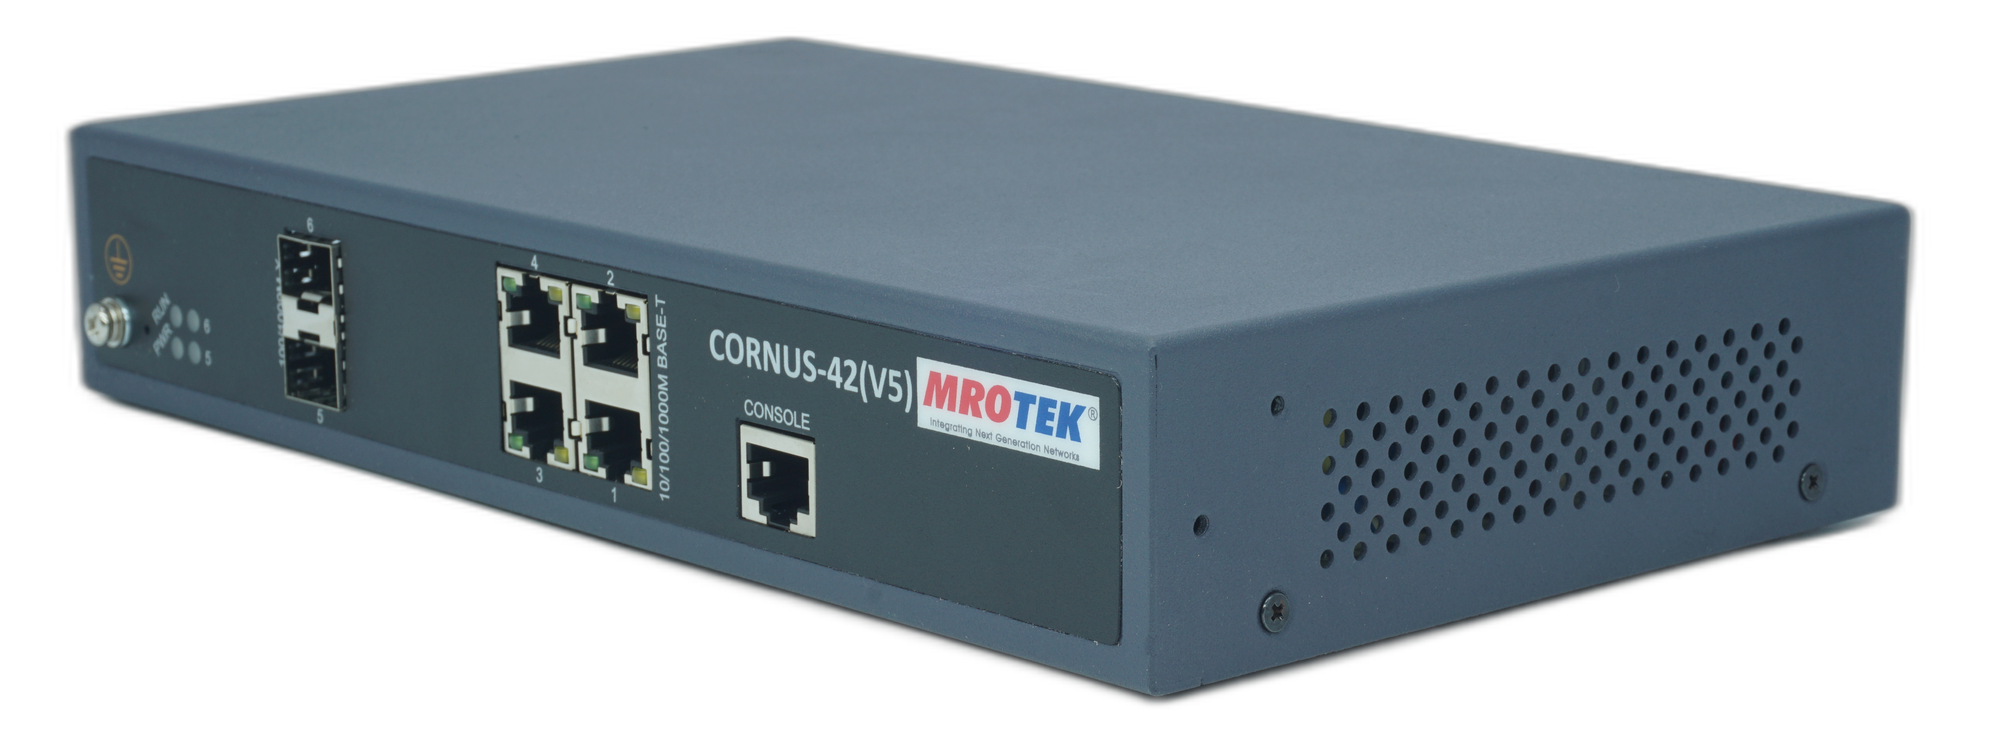
- 4× 10/100/1000M RJ45 Ethernet ports
- 2× 1G fibre uplink ports
- 1× RJ-45 console port
- 19-inch rack-mountable, 1RU form factor
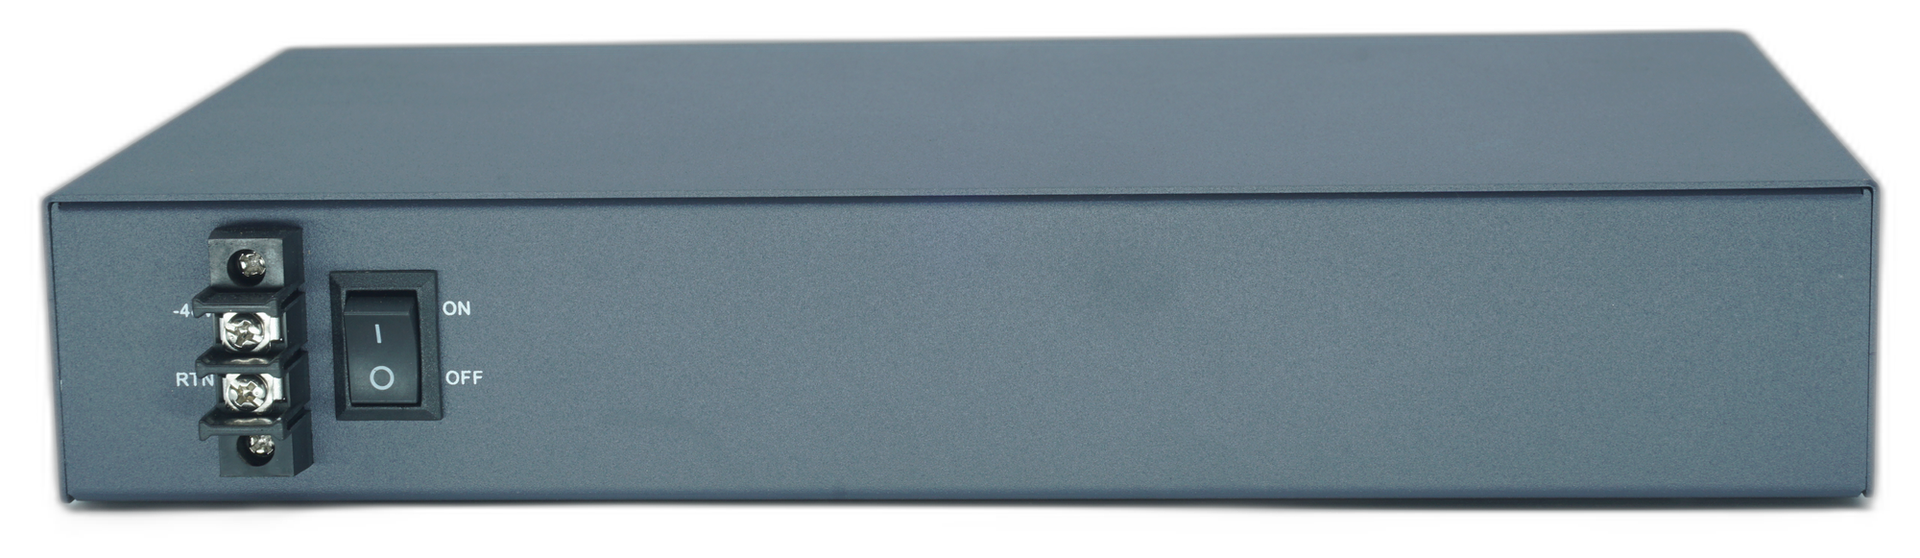
- Power supply — single AC/DC configurations
- 12 Gbps non-blocking switching capacity
- 8.9 Mpps forwarding rate
- 8K MAC address table (static and dynamic)
- IEEE 802.1Q VLAN — up to 4094 VLANs
- Store-and-forward switching
- IEEE 802.1Q VLAN, QinQ (802.1ad), private VLAN
- IEEE 802.3ad LACP link aggregation with port mirroring
- Spanning Tree: STP (802.1D), RSTP (802.1w), MSTP (802.1s) with BPDU guard and root guard
- IGMP snooping v1/v2/v3 for multicast traffic
- ITU-T G.8031/G.8032 ERPS Ethernet ring protection switching
- ACL — policy-based control by VLAN ID, source MAC/IP address, and protocol port
- Storm control for broadcast, multicast, and unicast traffic
- Port security with MAC address binding
- IP-MAC port binding
- IEEE 802.1x port-based authentication
- RADIUS and TACACS+ authentication
- IEEE 802.1p class of service (CoS)
- IP DSCP-based CoS
- Fragment and DSCP-based traffic classification
- Console, Telnet, SSH v2, Web GUI management
- SNMP v1/v2c/v3 with RMON
- Firmware image upgrade
- Managed via OmniEye NMS/EMS (optional)